找到 5 篇与 绿色软件 相关的结果
-
 ShuiZe_0x727 绿色软件分享 推荐一个实用的开源工具——ShuiZe_0x727。项目由0x727开发维护,GitHub上获得了 4023 个Star。简单来说,它是一款信息收集自动化工具,对于站长和开发者来说是个不错的工具。 工具功能介绍 郑重声明:文中所涉及的技术、思路和工具仅供以安全为目的的学习交流使用,任何人不得将其用于非法用途以及盈利等目的,否则后果自行承担。 0x01 介绍作者:Ske团队:0x727,未来一段时间将陆续开源工具,地址:https://github.com/0x727定位:协助红队人员快速的信息收集,测绘目标资产,寻找薄弱点语言:python3开发功能:一条龙服务,只需要输入根域名即可全方位收集相关资产,并检测漏洞。也可以输入多个域名、C段IP等,具体案例见下文。调用:脚本借用了ksubdomain爆破子域名和theHarvester收集邮箱,感谢ksubdomain和theHarvester作者 0x02 安装为了避免踩坑,建议安装在如下环境中* 当前用户对该目录有写权限,不然扫描结果无法生成。root权限即可 Python环境必须是3.7以上,因为使用了异步。建议VPS环境是ubuntu20,默认是python3.8。安装模块的时候切记不要走豆瓣的源 在配置文件iniFile/config.ini里加入api(fofa、shodan、github、virustotal)` chmod 777 build.sh ./build.sh `image-20210728153419131python3 ShuiZe.py -himage-20210728154929084 docker运行ShuiZe较多人反馈安装的时候会出现各种报错,新增通过docker运行ShuiZe通过下面的命令安装docker,然后拉取python3.8的容器,再git clone水泽后,运行docker_build.sh即可。` apt install docker.io docker pull yankovg/python3.8.2-ubuntu18.04 docker run -itd yankovg/python3.8.2-ubuntu18.04 bash docker exec -it docker的ID /bin/bash apt-get update apt install git --fix-missing apt install vim rm /usr/bin/python3 ln -s /usr/local/bin/python3.8 /usr/bin/python3 python3 -m pip install --upgrade pip git clone https://github.com/0x727/ShuiZe_0x727.git chmod 777 docker_build.sh ./docker_build.sh ## 0x03 效果展示备案反查顶级域名不是泛解析,调用ksubdomain爆破子域名theHarvest获取邮箱第三方数据接口 -> 获取子域名github -> 从github获取子域名,并把查询结果保存到txt,并匹配关键字获取敏感信息百度和必应爬虫证书子域名友链解析子域名A记录,检测是否CDN和整理C段的IP网络空间搜索引擎:Fofa和ShodanIP反查域名存活探测漏洞检测扫描结果保存在excel文件里excel的内容如下备案反查顶级域名邮箱Github敏感信息爬虫证书子域名A记录和CDN动态链接和后台地址网络空间搜索引擎ip反查域名存活网站标题指纹和漏洞相关域名和C段 ## 0x04 POC编写POC的模板文件例子:`Plugins/Vul/Web/__template__.py`只需要在run_detect方法里调用POC的利用方法即可。 ## 0x05 使用方法| 语法 | 功能 | | :------------------------------------------------------- | :-------------------------------------------- | | python3 ShuiZe.py -d domain.com | 收集单一的根域名资产 | | python3 ShuiZe.py --domainFile domain.txt | 批量跑根域名列表 | | python3 ShuiZe.py -c 192.168.1.0,192.168.2.0,192.168.3.0 | 收集C段资产 | | python3 ShuiZe.py -f url.txt | 对url里的网站漏洞检测 | | python3 ShuiZe.py --fofaTitle XXX大学 | 从fofa里收集标题为XXX大学的资产,然后漏洞检测 | | python3 ShuiZe.py -d domain.com --justInfoGather 1 | 仅信息收集,不检测漏洞 | | python3 ShuiZe.py -d domain.com --ksubdomain 0 | 不调用ksubdomain爆破子域名 | ## 0x06 实现原理* 备案反查顶级域名 -> 获取目标域名相关的其他根域名 -> 接口:http://icp.chinaz.com * 判断是否是泛解析 * 泛解析-> 不爆破子域名 * 不是泛解析 -> 调用ksubdomain爆破子域名(脚本里我用的是linux版本的ksubdomain,文件地址:./Plugins/infoGather/subdomain/ksubdomain/ksubdomain_linux,如果是其他系统请自行替换) * 调用theHarvester -> 获取子域名和邮箱列表 * 第三方数据接口 -> 获取子域名 * virustotal -> https://www.virustotal.com -> 需要api * ce.baidu.com -> http://ce.baidu.com * url.fht.im -> https://url.fht.im/ * qianxun -> https://www.dnsscan.cn/ * sublist3r -> https://api.sublist3r.com * crt.sh -> https://crt.sh * certspotter -> https://api.certspotter.com * bufferover -> http://dns.bufferover.run * threatcrowd -> https://threatcrowd.org * hackertarget -> https://api.hackertarget.com * chaziyu -> https://chaziyu.com/hbu.cn/ * rapiddns -> https://rapiddns.io * sitedossier -> http://www.sitedossier.com * ximcx -> http://sbd.ximcx.cn * github -> 从github获取子域名,并把查询结果保存到txt-获取敏感信息 * 敏感信息关键字匹配,可在iniFile/config.ini自定义关键字内容,内置如下关键字('jdbc:', 'password', 'username', 'database', 'smtp', 'vpn', 'pwd', 'passwd', 'connect') * 百度和必应爬虫 -> 获取目标后台等地址('inurl:admin', 'inurl:login', 'inurl:system', 'inurl:register', 'inurl:upload', '后台', '系统', '登录') * 证书 -> 获取目标关联域名 * 子域名友链 -> 获取未爆破出的子域名,未被收录的深层域名整理上面所有的子域名* 对所有子域名判断是否是CDN并解析出A记录* 统计每个c段出现IP的个数* 调用网络空间搜索引擎 * fofa -> 需要API * shodan -> 需要API* 前面获得的ip反查域名得到相关资产的子域名,整理出所有的子域名和IP* 整理所有资产探测漏洞* Web -> 存活探测* 获取标题 * 自动跑后台路径(['admin', 'login', 'system', 'manager', 'admin.jsp', 'login.jsp', 'admin.php', 'login.php','admin.aspx', 'login.aspx', 'admin.asp', 'login.asp']) * 如果URL是IP则查询IP的归属地 * 漏洞检测 -> Plugins/Vul/Web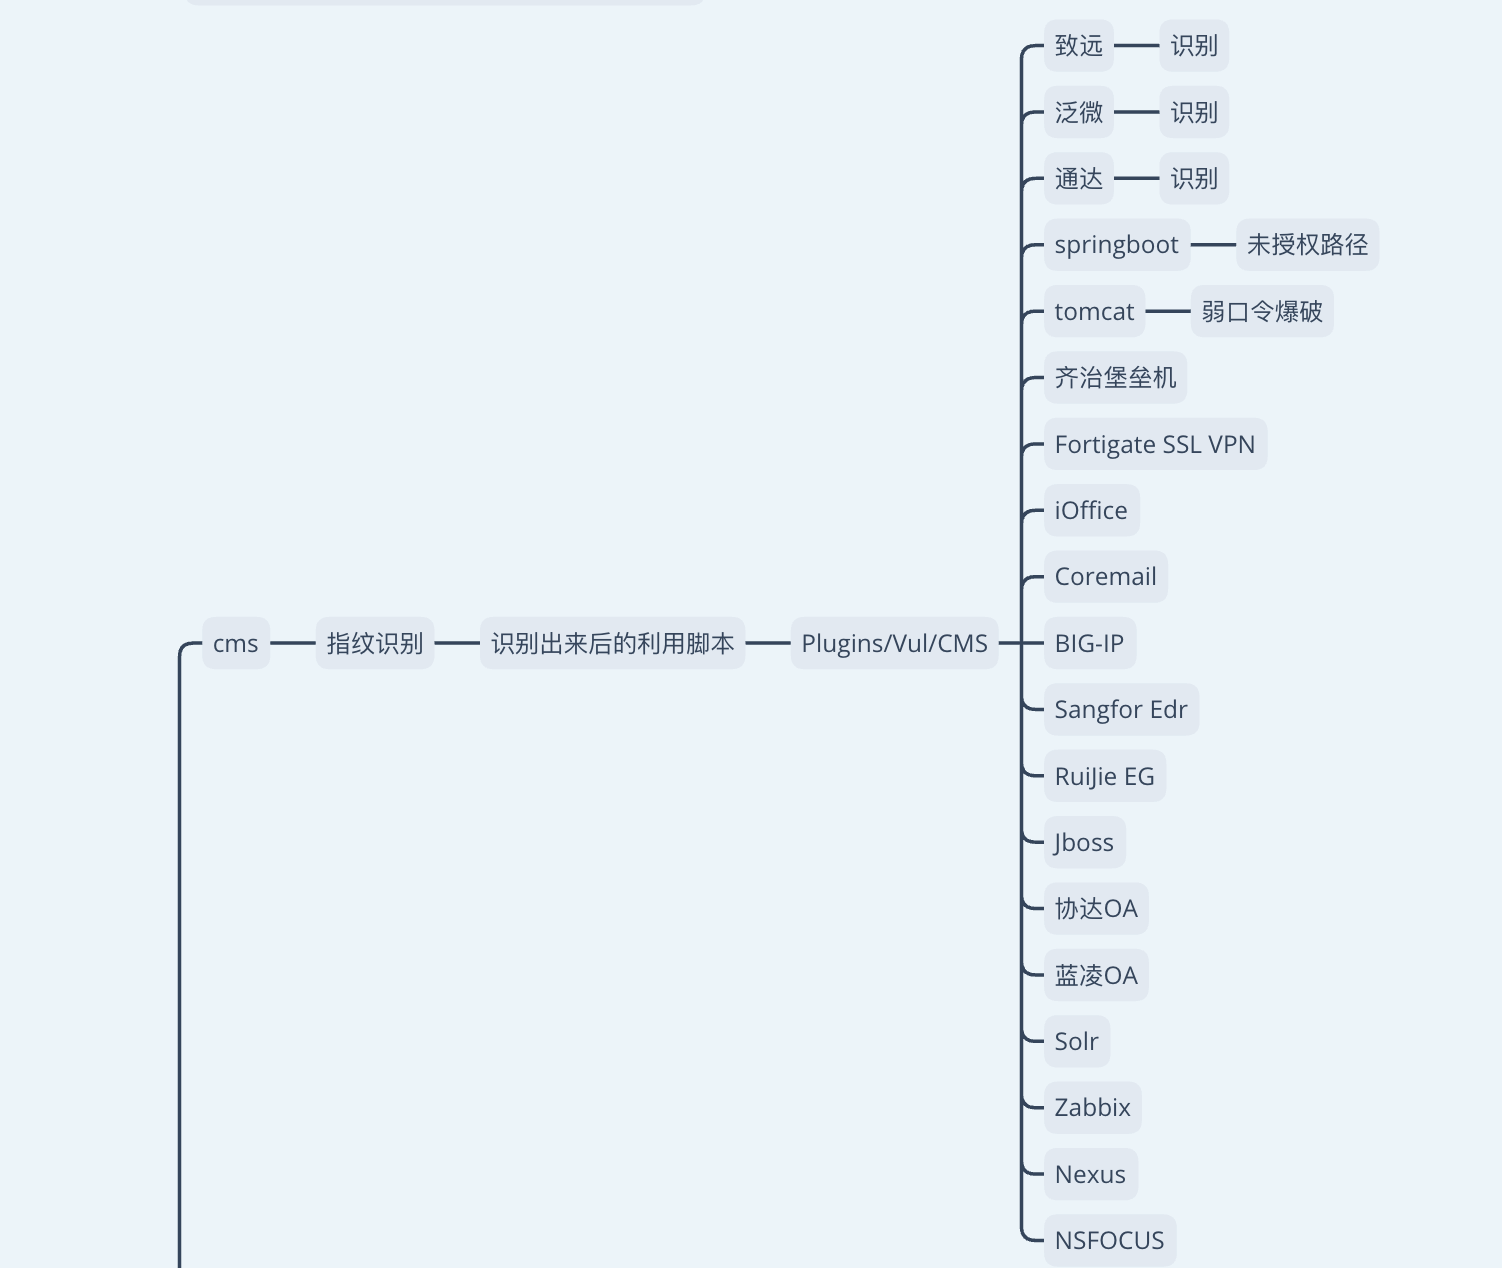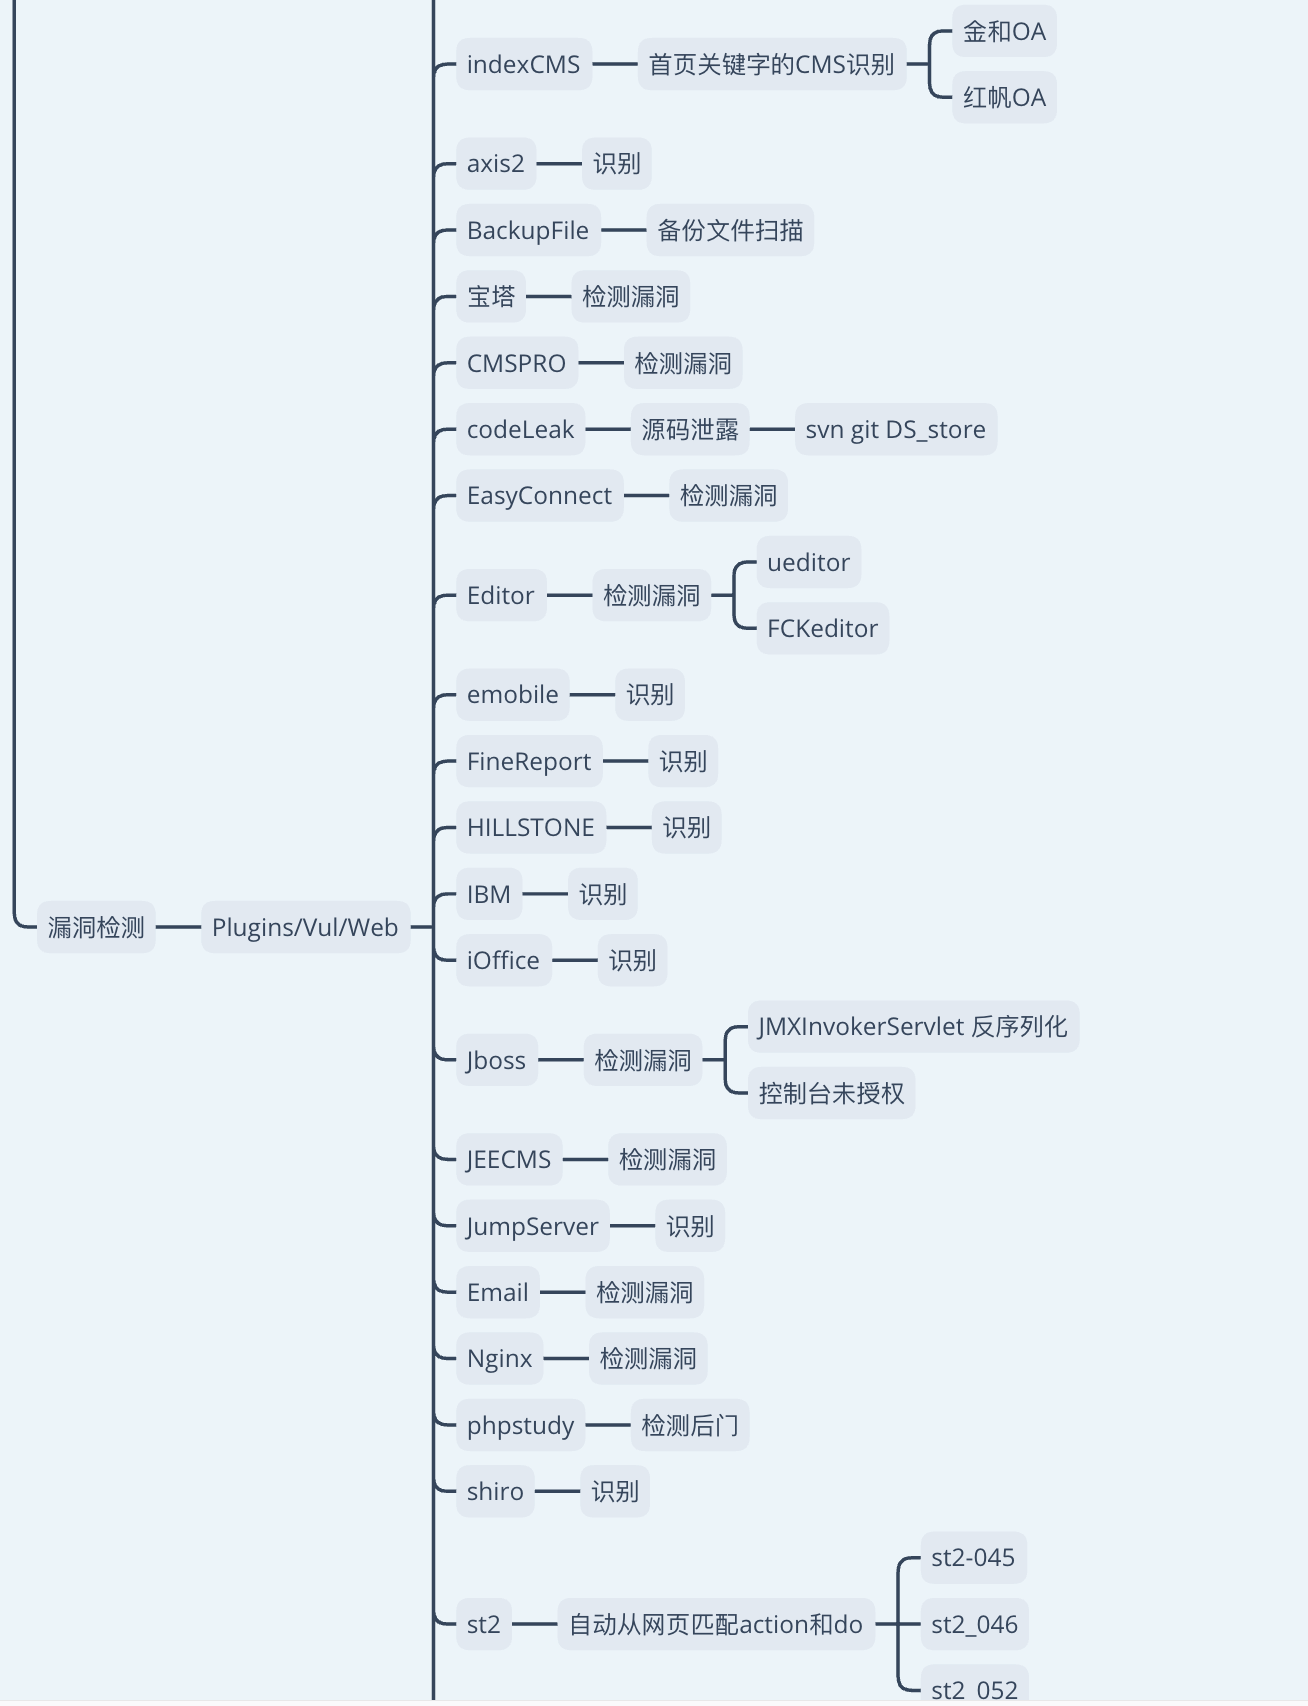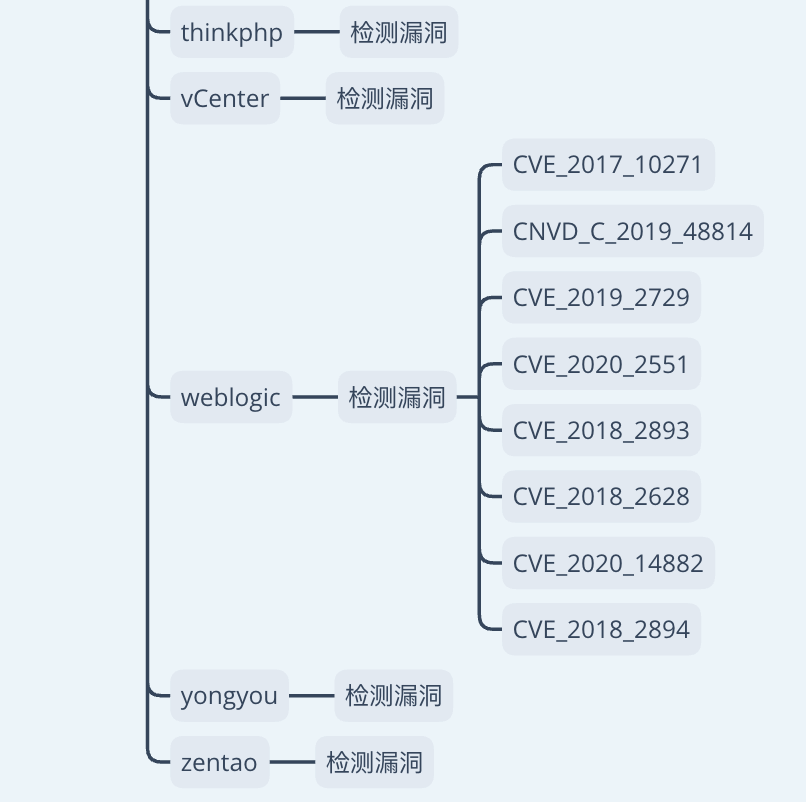* 非Web服务 --> 未授权和弱口令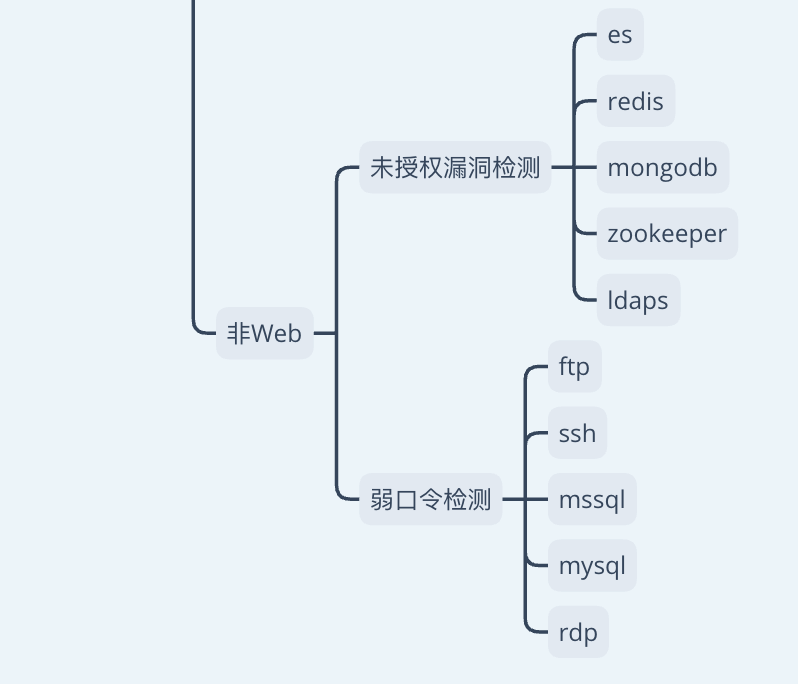其他功能结果展示:完整流程图:! ## 0x07 新增功能2021.7.31 增加了Censys接口,需要在iniFile/config.ini的[censys api]中填入API。 功能是获取域名的所有解析IP记录,一是为了Host碰撞,二是更加准确的得到C段IP需要censys的api,免费的账户一个月只有250次查询,所以后期需要注意,用完了要更新api2021.7.31 增加了Host碰撞访问内网系统漏洞,感谢 **横戈安全团队-小洲** 提交的建议!2021.8.1 修复了CDN判断的bug,感谢 **leveryd 师傅** 提交的bug。issues地址:https://github.com/0x727/ShuiZe_0x727/issues/32021.8.3 修复了chinazApi接口请求超时太长的bug,设置默认时间10秒,感谢 **k0njac 师傅**提交的bug。issues地址:https://github.com/0x727/ShuiZe_0x727/issues/112021.8.13 增加了获取Github敏感信息地址的作者邮箱,帮助判断是否是目标员工的项目2021.8.17 更新了ksubdomain版本,自动选择网卡,不需要重新手动输入网卡ksubdomain项目地址:https://github.com/knownsec/ksubdomain!2021.9.1 增加了从fofa中爬去socks代理功能,后续可以手动配合proxychains进行漏洞探测,防止因为被封IP导致漏报。感谢 **安恒水滴实验室-1amfine2333师傅** 提供的思路。!2021.9.2 增加了Confluence指纹识别,漏洞利用地址:https://github.com/h3v0x/CVE-2021-26084_Confluence2021.9.4 增加了某查接口,对目标的整个架构分析,涵盖【对外投资、控股公司、分支机构、联系方式、邮箱】等信息。感谢 **pykiller师傅** 提交的建议,同时参考了 **吐司师傅gubeiya** 的脚本issues地址:https://github.com/0x727/ShuiZe_0x727/issues/25!2021.9.26 增加了夸克的api接口,-d -c --fofaTitle中都会调用限定了每次最大查询数量1000条,不然一个月5w条数据也用不了多少次在config.ini配置文件的quake_nums值issues地址:https://github.com/0x727/ShuiZe_0x727/issues/33!!2021.11.30 增加了奇安信hunter的api接口,-d -c --fofaTitle中都会调用限定了每次最大查询数量200条,不然一天的几千条数据也用不了多少次在config.ini配置文件的qianxin_nums值issues地址:https://github.com/0x727/ShuiZe_0x727/issues/48!!2022.1.17 修复了certspotter接口获取子域名过滤不严谨的问题感谢 **union-cmd师傅** 提交的建议issues地址:https://github.com/0x727/ShuiZe_0x727/issues/572022.3.21 更新了fofa api的域名2022.3.21 更新了域名备案反查的问题2022.3.23 增加了securitytrails接口获取子域名,该接口很强大,建议在config.ini里添加你的api keysissues地址:https://github.com/0x727/ShuiZe_0x727/issues/48注册地址: https://docs.securitytrails.com/!感谢 **郭师傅** 提交的建议2022.3.23 修复了爱企查无法获取数据的问题感谢 **横戈安全团队-chhyx(逗逗)** 的技术支持2022.4.13 修复了奇安信测绘语法使用错误的问题issues地址:https://github.com/0x727/ShuiZe_0x727/issues/74感谢 **cwkiller** 反馈的问题2022.4.16 增加了调用Nuclei检测漏洞nuclei的参数在iniFile/config.ini配置,默认为`nuclei_config = -rl 300 -c 50 -timeout 5 -stats -silent -severity critical,high` 根据需求自行修改!2022.7.5 Nuclei默认参数配置增加-asissues地址: https://github.com/0x727/ShuiZe_0x727/issues/104-as 参数,先使用 wappalyzer 进行指纹识别,在进行扫描。感谢 **anquanbiji** 反馈的建议2022.8.12 ShuiZe增加Dockerfile安装方式issues地址: https://github.com/0x727/ShuiZe_0x727/issues/99感谢 [@1itt1eB0y](https://github.com/1itt1eB0y) 提供的脚本。**安全性自行评估**2022.8.12 修复了大量反馈aiqicha脚本报错的问题,初步排查是被封IP的原因。2022.8.12 修复了quakeApi没有title导致报错的情况issues地址: https://github.com/0x727/ShuiZe_0x727/issues/120感谢 **Zimba5880** 反馈的建议2022.8.20 增加了快代理配置,漏洞检测时会使用快代理的代理池,这样可以避免当前IP被封后导致后续的扫描出现遗漏。购买快代理的隧道代理,地址:https://www.kuaidaili.com/cart?t=tps_c根据自己的需求选择包年包月或者按量付费,更换IP的频率。这里注意并发请求数的,并发数量越高,在配置文件里iniFile/config.ini的thread_num就可以设置的更高。假设并发数为5,那么thread_num不要设置超过10,具体的值自己测试。!购买后查看host、port、username、password,然后填入到配置文件里!!默认关闭快代理代理池功能,如果要开启,把switch设置为on,使用快代理代理池时会先验证是否配置正确!2022.8.27 集成了ObserverWard扫描指纹项目地址:https://github.com/0x727/ObserverWard指纹地址:https://github.com/0x727/FingerprintHub! ## 0x08 反馈ShuiZe(水泽) 是一个免费且开源的项目,我们欢迎任何人为其开发和进步贡献力量。* 在使用过程中出现任何问题,可以通过 issues 来反馈。 * Bug 的修复可以直接提交 Pull Request 到 dev 分支。 * 如果是增加新的功能特性,请先创建一个 issue 并做简单描述以及大致的实现方法,提议被采纳后,就可以创建一个实现新特性的 Pull Request。 * 欢迎对说明文档做出改善,帮助更多的人使用 ShuiZe。 * 贡献代码请提交 PR 至 dev 分支,master 分支仅用于发布稳定可用版本。*提醒:和项目相关的问题最好在 issues 中反馈,这样方便其他有类似问题的人可以快速查找解决方法,并且也避免了我们重复回答一些问题。* ## Stargazers over time <!--more--> {card-default label="? 工具信息"} ? 项目地址:[https://github.com/0x727/ShuiZe_0x727](https://github.com/0x727/ShuiZe_0x727) ⭐ Star数:4023 ? 开发语言:Python ? 项目描述:信息收集自动化工具 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/0x727/ShuiZe_0x727/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/0x727/ShuiZe_0x727"} 总的来说,**ShuiZe_0x727**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。

-
metasploit-framework 绿色软件分享 推荐一个实用的开源工具——metasploit-framework。项目由rapid7开发维护,GitHub上获得了 39007 个Star。简单来说,它是一款Metasploit框架,对于站长和开发者来说是个不错的工具。 工具功能介绍 The Metasploit Framework is an open-source tool released under a BSD-style license. For detailed licensing information, refer to the COPYING file. Latest Version Access the latest version of Metasploit from the Nightly Installers page. Documentation Comprehensive documentation, including usage guides, is available at Metasploit Docs. Development Environment To set up a development environment, visit the Development Setup Guide. Bug and Feature Requests Submit bugs and feature requests via the GitHub Issues tracker. New submissions can be made through the MSF-BUGv1 form. API Documentation For information on writing modules, refer to the API Documentation. Support and Communication For questions and suggestions, you can:- Join our GitHub Discussions for community support and general questions Join the Metasploit Slack for real-time chat Submit GitHub Issues for bug reports and feature requests Follow @metasploit on X or @metasploit@infosec.exchange on Mastodon for updatesNote: Some community members may still use IRC channels and the metasploit-hackers mailing list, though the primary support channels are now GitHub Discussions and Slack. Installing Metasploit Recommended InstallationWe recommend installation with the official Metasploit installers on Linux or macOS. Metasploit is also pre-installed with Kali.For a manual setup, consult the Dev Environment Setup guide. Using MetasploitTo get started with Metasploit:1. Start msfconsole: This is the primary interface for interacting with Metasploit. Explore Resources: Visit the Using Metasploit section of the documentation. ContributingTo contribute to Metasploit:1. Setup Development Environment: Follow the instructions in the Development Setup Guide on GitHub. Clone the Repository: Obtain the source code from the official repository. Submit a Pull Request: After making changes, submit a pull request for review. Additional details can be found in the Contributing Guide. {card-default label="? 工具信息"} ? 项目地址:https://github.com/rapid7/metasploit-framework ⭐ Star数:39007 ? 开发语言:Ruby ? 项目描述:Metasploit框架 {/card-default} {cloud type="default" title="网盘下载" url="https://github.com/rapid7/metasploit-framework/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/rapid7/metasploit-framework"} 总的来说,metasploit-framework是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。
-
fscan 绿色软件分享 推荐一个实用的开源工具——**fscan**。项目由shadow1ng开发维护,GitHub上获得了 **14514** 个Star。简单来说,它是一款一款内网综合扫描工具方便一键自动化、全方位漏扫扫描。(内网综合扫描工具,实现一键自动化、全方位漏洞扫描),对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 [English](README_EN.md)内网综合扫描工具,一键自动化漏扫。**版本**: 2.2.1 ## 功能特性 ### 扫描能力 - **主机发现** - ICMP/Ping存活探测,支持大网段B/C段存活统计 - **端口扫描** - TCP全连接扫描,内置133个常用端口,支持端口组(web/db/service/all) - **服务识别** - 智能协议识别,支持20+种服务指纹匹配 - **Web探测** - 网站标题、CMS指纹、Web中间件、WAF/CDN识别(40+指纹)### 爆破能力 - **弱密码爆破** - 28种服务爆破(SSH/RDP/SMB/FTP/MySQL/MSSQL/Oracle/Redis等) - **Hash碰撞** - 支持NTLM Hash认证(SMB/WMI) - **SSH密钥登录** - 支持私钥认证方式 - **智能字典** - 内置100+常见弱密码,支持{user /}变量替换### 漏洞检测 - **高危漏洞** - MS17-010(永恒之蓝)、SMBGhost(CVE-2020-0796) - **未授权访问** - Redis/MongoDB/Memcached/Elasticsearch等未授权检测 - **POC扫描** - 集成Web漏洞POC,支持Xray POC格式 - **DNSLog** - 支持DNSLog外带检测### 漏洞利用 - **Redis利用** - 写公钥、写计划任务、写WebShell、主从复制RCE - **MS17-010利用** - ShellCode注入,支持添加用户、执行命令 - **SSH命令执行** - 认证成功后自动执行命令### 本地模块 - **信息收集** - 系统信息、环境变量、域控信息、网卡配置 - **凭据获取** - 内存转储(MiniDump)、键盘记录、注册表导出 - **权限维持** - Systemd服务、Windows服务、计划任务、启动项、LD_PRELOAD - **反弹Shell** - 正向Shell、反向Shell、SOCKS5代理服务 - **杀软检测** - 识别目标主机安装的安全软件 - **痕迹清理** - 日志清理工具### 输入输出 - **目标输入** - IP/CIDR/域名/URL,支持文件批量导入 - **排除规则** - 支持排除特定主机、端口 - **输出格式** - TXT/JSON/CSV多格式输出 - **静默模式** - 无Banner、无进度条、无颜色输出### 网络控制 - **代理支持** - HTTP/SOCKS5代理,支持指定网卡 - **发包控制** - 速率限制、最大发包数量控制 - **超时控制** - 端口超时、Web超时、全局超时独立配置 - **并发控制** - 端口扫描线程、服务扫描线程独立配置### 扩展功能 - **SDK嵌入** - `pkg/fscan`提供Go SDK,可嵌入Agent或安全平台,支持任务控制(Pause/Resume)、实时进度回调、TaskID追溯 - **Web管理界面** - 可视化扫描任务管理(条件编译 -tags web) - **Lab靶场环境** - 内置Docker靶场用于测试学习 - **插件化架构** - 服务插件/Web插件/本地插件分离,易于扩展 - **多语言支持** - 中英文界面切换(-lang zh/en) - **性能统计** - JSON格式性能报告(-perf)## v2.1.0 更新日志> 本次更新包含 **262个提交**,涵盖30项新功能、120项修复、54项重构、14项性能优化、20项测试增强。 ### 架构重构 - **全局变量消除** - 迁移至Config/State对象,提升并发安全和可测试性 - **SMB插件融合** - 整合smb/smb2/smbghost/smbinfo为统一插件,新增smb_protocol.go - **服务探测重构** - 实现Nmap风格fallback机制,优化端口指纹识别策略 - **输出系统重构** - TXT实时刷盘+双写机制,解决结果丢失和乱序问题 - **i18n框架升级** - 迁移至go-i18n,完整覆盖core/plugins/webscan模块 - **HostInfo重构** - Ports字段从string改为int,类型安全 - **函数复杂度优化** - clusterpoc(125→30)、EnhancedPortScan(111→20) - **代码审计** - 修复P0-P2级别问题,清理deadcode - **日志系统优化** - LogDebug调用清理(71→18),精简启动日志输出### 性能优化 - **正则预编译** - 全局正则表达式预编译,避免重复编译开销 - **内存优化** - map[string]bool改为map[string]struct{}节省内存 - **并发指纹匹配** - 多协程并行匹配,提升识别速度 - **连接复用** - SOCKS5全局拨号器复用,避免重复握手 - **滑动窗口调度** - 自适应线程池+流式迭代器,优化端口扫描 - **CEL缓存优化** - POC扫描CEL环境缓存,减少重复初始化 - **包级变量提取** - proxyFailurePatterns/resourceExhaustedPatterns/sslSecondProbes等 - **预分配容量** - 简化转换链、单次字符串替换 - **并发安全优化** - 优化锁粒度和内存分配### 新功能 - **Web管理界面** - 可视化扫描任务管理,响应式布局和进度显示 - **多格式POC适配** - 支持xray和afrog格式POC - **智能扫描模式** - 布隆过滤器去重+代理优化 - **增强指纹库** - 集成FingerprintHub(3139条指纹) - **Favicon指纹识别** - 支持mmh3和MD5双格式hash匹配 - **通用版本提取器** - 自动提取服务版本信息 - **指纹优先级排序** - 智能排序匹配结果 - **智能协议检测** - 自动识别HTTP/HTTPS协议类型 - **网卡指定功能** - 支持VPN场景(-iface参数) - **排除主机文件** - 支持从文件读取排除主机(-ehf参数) - **ICMP令牌桶限速** - 防止高速扫描导致路由器崩溃 - **端口扫描重试** - 失败自动重扫机制 - **RDP真实认证** - 集成grdp库实现系统指纹识别 - **SMB/FTP文件列表** - 匿名访问时自动列出文件 - **302跳转双重识别** - 同时识别原始响应和跳转后响应指纹 - **TXT输出URL汇总** - 末尾添加Web服务URL列表便于批量测试 - **nmap核心集成** - 三大改进:探测策略/匹配引擎/版本解析 - **插件选择性编译** - Build Tags系统,支持服务/本地/Web插件独立编译 - **默认端口扩展** - 从62个扩展到133个常用端口 - **全端口扫描支持** - 扩大端口范围限制 - **HTTP重定向控制** - 可配置的重定向次数限制 - **性能分析支持** - 添加pprof性能分析和benchmark测试 - **TCP包统计** - 服务插件支持TCP包发送统计 - **fscan-lab靶场** - 内网渗透训练平台,覆盖全部漏洞场景(未完成) - **Redis利用增强** - 移植完整Redis利用功能(写公钥/计划任务/WebShell/主从RCE) - **rsync插件重构** - 使用go-rsync库重构认证逻辑### Bug修复(120项,列出关键修复) - **RDP空指针panic** - 修复证书解析导致的崩溃(#551) - **批量扫描漏报** - 修复大规模扫描遗漏问题(#304) - **JSON输出格式** - 修复输出格式错误(#446) - **Redis弱密码检测** - 修复检测遗漏问题(#447) - **结果实时保存** - 修复扫描结果未及时保存(#469) - **Nmap解析溢出** - 修复八进制转义解析bug(#478) - **指纹识别竞态** - 修复webtitle/webpoc竞态问题(#474) - **MySQL连接验证** - 改用information_schema库验证 - **代理端口误判** - 修复代理模式下端口状态判断错误 - **Context超时** - 修复22处插件超时未响应问题 - **ICMP竞态条件** - 修复并发扫描竞争问题 - **IPv6地址格式** - 修复4处地址格式化问题 - **POC高并发卡死** - 修复Context未传播问题 - **Ctrl+C结果丢失** - 添加信号处理确保结果写入 - **SOCKS5全回显** - 添加代理连接验证 - **服务探测泄漏** - 修复连接未正确关闭问题 - **webtitle响应丢弃** - 修复部分响应数据被丢弃导致识别失败 - **TXT漏洞信息缺失** - 修复输出遗漏漏洞详情 - **JSON指纹缺失** - 统一SERVICE结果Target格式 - **扫描耗时显示** - 修复完成耗时显示为0的问题 - **虚假漏洞记录** - 重构TXT输出系统消除误报 - **Redis跨平台路径** - 修复利用功能的路径和超时问题 - **Windows编译警告** - 修复fscan-lite平台兼容性 - **Go 1.20兼容** - 降级依赖保持兼容性### 测试增强(20项) - **单元测试** - 核心模块覆盖率74-100% - **并发安全测试** - State对象、指纹匹配引擎专项测试 - **集成测试** - Web扫描/端口扫描/服务探测/SSH认证/ICMP探测 - **CLI参数测试** - 命令行参数解析验证 - **性能基准测试** - AdaptivePool、服务探测策略benchmark - **ResultBuffer测试** - 去重和完整度评分验证### 工程化改进 - **CI流程优化** - golangci-lint v2升级,简化构建步骤 - **Issue自动化** - GitHub Issue模板优化,Project自动化工作流 - **Lint全量修复** - revive/errcheck/shadow/staticcheck/gosimple全部通过 - **README重写** - 中英文文档全面更新 - **代码格式统一** - gofmt/goimports规范化## 快速开始 bash # 扫描C段 ./fscan -h 192.168.1.1/24 # 指定端口 ./fscan -h 192.168.1.1 -p 22,80,443,3389 # 仅存活探测 ./fscan -h 192.168.1.1/24 -ao # 禁用爆破 ./fscan -h 192.168.1.1/24 -nobr # Web扫描 ./fscan -u http://192.168.1.1 # 本地插件 ./fscan -local systeminfo # Hash碰撞 ./fscan -h 192.168.1.1 -m smb2 -user admin -hash xxxxx # Redis写公钥 ./fscan -h 192.168.1.1 -m redis -rf id_rsa.pub ## 编译 bash # 标准编译 go build -ldflags="-s -w" -trimpath -o fscan . # 带Web管理界面 go build -tags web -ldflags="-s -w" -trimpath -o fscan-web . ## 安装 bash # Arch Linux yay -S fscan-git ## 运行`fscan.exe -h 192.168.x.x` !!`fscan.exe -h 192.168.x.x -rf id_rsa.pub` (Redis写公钥) !`fscan.exe -h 192.168.x.x -m ssh -user root -pwd password` !`fscan.exe -h 192.168.x.x -m ssh -user root -pwda pass1 pass2 pass3` (追加多个密码)`fscan.exe -h 192.168.x.x -p80 -proxy http://127.0.0.1:8080` !`fscan.exe -h 192.168.x.x -socks5 socks5://user:pass@127.0.0.1:1080` (SOCKS5认证代理)`fscan.exe -h 192.168.x.x -p 139 -m netbios` !!`fscan.exe -h 192.0.0.0/8 -m icmp` .png](/live.png)## 路线图 ### 更新计划 - **更新周期** - 每月一次版本发布 - **前两周** - 新功能开发与特性更新 - **后两周** - Bug修复与代码整合 - **欢迎PR** - 期待您的贡献!### SDK & Agent 集成 - 扩展SDK能力,完善端侧Agent嵌入支持 - 断点续扫、带宽级限速、内存水位控制 - 更多Agent场景的集成示例### 插件生态 - 持续扩展服务插件覆盖范围 - 为每个服务插件开发更多漏洞检测和利用能力 - 保持插件API向后兼容,确保旧版本POC持续可用### Fscan-lite - C语言重写的轻量版本 - 更小的体积,更少的依赖 - 支持更多嵌入式/受限环境 - 目录: [fscan-lite](./fscan-lite)### Fscan-lab - 内网渗透测试靶场环境 - 覆盖所有fscan支持的漏洞场景 - 开发测试与功能验证平台 - 新手学习与技能练习环境 - 目录: [fscan-lab](./fscan-lab)##
-
分享一个不错的绿色软件:antSword 在寻找好用的工具软件时,发现了antSword这个项目。它的定位是mirror https://github.com/AntSwordProject/antSword,目前在Gitee上已经积累了14个Star,更新也比较活跃,最后更新时间是2024年04月17日。下面来详细了解一下这个工具的功能特点。 工具功能介绍 AntSword in your hands, no worries in your mind!AntSword is an open source, cross-platform website administration tool, being designed to meet the needs of penetration testers together with security researchers with permissions and/or authorizations as well as webmasters. Anyone shall not use it for illegal purposes and profitability. Besides that, publishing unauthorized modified version is also prohibited, or otherwise bear legal responsibilities. This software, of which the development thought is modularization, is intended to provide easy-to-understand codes and modification guidelines for users of different levels. Therefore, any contribution making by everyone to this project is encouraged, whether large or small. By doing so, this tool can be more convenient and consequently become your most powerful kit! 中文说明 / Document / Changelog Development stack Electron ES6 dhtmlx Nodejs And other libraries called in the project. Screenshots [url-mainui] More Screenshots [url-filemanager] [url-terminal] [url-database] [url-pluginstore] Quick Start See document: Quick Start Contribute See document: Make contributions to AntSword Thanks Thanks to anyone who made any contributions.Other 404StarLink 2.0 - Galaxy ! antSword has joined 404Team 404StarLink 2.0 - Galaxy LICENSE LICENSE 总的来说,antSword是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一个mirror https://github.com/AntSwordProject/antSword的解决方案,不妨下载试试。使用前建议仔细阅读项目文档。 {card-default label="? 工具信息" /} ? 工具名称:antSword ? 开发作者:medicean ? 工具描述:mirror https://github.com/AntSwordProject/antSword ? 开发语言:未知 ? 开源协议:未知开源协议 ⭐ Star数:14 | ? Fork数:14 ? 更新时间:2024年04月17日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/AntSwordProject/antSword/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/AntSwordProject/antSword.git"}
-
免费开源绿色软件推荐:fuzzdb-collect 下载 推荐一个实用的开源工具——fuzzdb-collect。项目由euphratica开发维护,采用未知开源协议发布。简单来说,它是一个网络上安全资源的搜集,对于站长和开发者来说是个不错的工具。 工具功能介绍 项目简介 Scanners Box是一个集合github平台上的安全行业从业者自研开源扫描器的仓库,包括子域名枚举、数据库漏洞扫描、弱口令或信息泄漏扫描、端口扫描、指纹识别以及其他大型扫描器或模块化扫描器,同时该仓库只收录各位网友自己编写的一般性开源扫描器,类似awvs、nmap、w3af等知名扫描工具不收录。 恶意软件 https://github.com/deadPix3l/CryptSky/ (勒索软件) DDOS防护 https://github.com/ywjt/Dshield waf开源及规则 https://github.com/SpiderLabs/ModSecurity https://github.com/xsec-lab/x-waf https://github.com/loveshell/ngx_lua_waf https://github.com/SpiderLabs/owasp-modsecurity-crs/tree/master/base_rules 入门指南 https://wizardforcel.gitbooks.io/web-hacking-101/content/ Web Hacking 101 中文版 https://wizardforcel.gitbooks.io/asani/content/ 浅入浅出Android安全 中文版 https://wizardforcel.gitbooks.io/lpad/content/ Android 渗透测试学习手册 中文版 https://wizardforcel.gitbooks.io/kali-linux-web-pentest-cookbook/content/ Kali Linux Web渗透测试秘籍 中文版 https://github.com/hardenedlinux/linux-exploit-development-tutorial Linux exploit 开发入门 https://www.gitbook.com/book/t0data/burpsuite/details burpsuite实战指南 http://www.kanxue.com/?article-read-1108.htm=&winzoom=1 渗透测试Node.js应用 https://github.com/qazbnm456/awesome-web-security Web安全资料和资源列表 https://sec-wiki.com/ sec-wiki安全维基百科 fuzz工具收集 https://github.com/ivanfratric/winafl https://github.com/attekett/NodeFuzz https://github.com/google/oss-fuzz http://blog.topsec.com.cn/ad_lab/alphafuzzer/ http://llvm.org/docs/LibFuzzer.html 子域名枚举扫描器或爆破工具 https://github.com/n4xh4ck5/N4xD0rk (利用搜索引擎来搜集子域名,可以使用西班牙语搜集) https://github.com/jonluca/Anubis https://github.com/lijiejie/subDomainsBrute (lijiejie开发的一款使用广泛的子域名爆破枚举工具) https://github.com/ring04h/wydomain (猪猪侠开发的一款域名收集全面、精准的子域名枚举工具) https://github.com/le4f/dnsmaper (子域名枚举爆破工具以及地图位置标记) https://github.com/0xbug/orangescan (提供web界面的在线子域名信息收集工具) https://github.com/TheRook/subbrute (高效精准的子域名爆破工具,同时也是扫描器中最常用的子域名API库) https://github.com/We5ter/GSDF (基于谷歌SSL透明证书的子域名查询脚本) https://github.com/mandatoryprogrammer/cloudflare_enum (使用CloudFlare进行子域名枚举的脚本) https://github.com/guelfoweb/knock (Knock子域名获取,可用于查找子域名接管漏洞) https://github.com/exp-db/PythonPool/tree/master/Tools/DomainSeeker (多方式收集目标子域名信息) https://github.com/code-scan/BroDomain (兄弟域名查询) https://github.com/chuhades/dnsbrute (高效的子域名爆破工具) https://github.com/yanxiu0614/subdomain3 (一款高效的子域名爆破工具) https://github.com/michenriksen/aquatone (子域名枚举、探测工具。可用于子域名接管漏洞探测) https://github.com/evilsocket/dnssearch (一款子域名爆破工具) https://github.com/reconned/domained (可用于子域名收集的一款工具) https://github.com/bit4woo/Teemo (域名收集及枚举工具) https://github.com/laramies/theHarvester ( https://github.com/swisskyrepo/Subdomino (子域名枚举,端口扫描,服务存活确认) https://github.com/nmalcolm/Inventus (通过爬虫实现的子域名收集工具) https://github.com/aboul3la/Sublist3r (快速子域枚举工具) 数据库类漏洞扫描器或爆破工具 https://github.com/0xbug/SQLiScanner (一款基于SQLMAP和Charles的被动SQL注入漏洞扫描工具) https://github.com/sqlmapproject/sqlmap (注入工具之王sqlmap) https://github.com/stamparm/DSSS (99行代码实现的sql注入漏洞扫描器) https://github.com/LoRexxar/Feigong (针对各种情况自由变化的MySQL注入脚本) https://github.com/youngyangyang04/NoSQLAttack (一款针对mongoDB的攻击工具) https://github.com/Neohapsis/bbqsql (SQL盲注利用框架) https://github.com/NetSPI/PowerUpSQL (攻击SQLSERVER的Powershell脚本框架) https://github.com/WhitewidowScanner/whitewidow (一款数据库扫描器) https://github.com/stampery/mongoaudit (MongoDB审计及渗透工具) https://github.com/torque59/Nosql-Exploitation-Framework (NoSQL扫描/爆破工具) https://github.com/missDronio/blindy (MySQL盲注爆破工具) https://github.com/fengxuangit/Fox-scan (基于SQLMAP的主动和被动资源发现的漏洞扫描工具) https://github.com/NetSPI/PowerUpSQL (用于SQL Server审计的powershell脚本) https://github.com/JohnTroony/Blisqy (用于- http header中的时间盲注爆破工具,仅针对MySQL/MariaDB) https://github.com/ron190/jsql-injection (Java 编写的SQL注入工具) https://github.com/Hadesy2k/sqliv (基于搜索引擎的批量SQL注入漏洞扫描器) https://github.com/UltimateHackers/sqlmate (在sqlmap基础上增加了目录扫描、hash爆破等功能) 弱口令/弱用户名扫描器或爆破工具 https://github.com/lijiejie/htpwdScan (一个简单的- http暴力破解、撞库攻击脚本) https://github.com/ysrc/F-Scrack (对各类服务进行弱口令检测的脚本) https://github.com/Mebus/cupp (根据用户习惯生成弱口令探测字典脚本) https://github.com/netxfly/crack_ssh (Go写的协程版的ssh edis\mongodb弱口令破解工具) https://github.com/LandGrey/pydictor (暴力破解字典建立工具) https://github.com/shengqi158/weak_password_detect (多线程探测弱口令) https://github.com/UltimateHackers/Blazy (支持测试 CSRF, Clickjacking, Cloudflare and WAF的弱口令探测器) 物联网设备识别工具或扫描器 https://github.com/reverse-shell/routersploit (路由器漏洞利用框架) https://github.com/jh00nbr/Routerhunter-2.0 (路由器漏洞扫描利用) https://github.com/RUB-NDS/PRET (打印机攻击框架) https://github.com/rapid7/IoTSeeker (物联网设备默认密码扫描检测工具) https://github.com/shodan-labs/iotdb (使用nmap扫描IoT设备) https://github.com/googleinurl/RouterHunterBR (路由器设备漏洞扫描利用) https://github.com/scu-igroup/telnet-scanner (Telnet服务密码撞库) 反射型或DOM-Based XSS扫描器 https://github.com/shawarkhanethicalhacker/BruteXSS (一款XSS扫描器,可暴力注入参数) https://github.com/1N3/XSSTracer (小型XSS扫描器,也可检测CRLF、XSS、点击劫持的) https://github.com/0x584A/fuzzXssPHP (PHP版本的反射型xss扫描) https://github.com/chuhades/xss_scan (批量扫描XSS的python脚本) https://github.com/BlackHole1/autoFindXssAndCsrf (自动化检测页面是否存在XSS和CSRF漏洞的浏览器插件) https://github.com/shogunlab/shuriken (使用命令行进行XSS批量检测) https://github.com/UltimateHackers/XSStrike (可识别并绕过WAF的XSS扫描工具) https://github.com/stamparm/DSXS (支持GET、POST方式的高效XSS扫描器) 企业资产管理或信息泄露搜集工具 https://github.com/ysrc/xunfeng (网络资产识别引擎,漏洞检测引擎) https://github.com/laramies/theHarvester (企业被搜索引擎收录敏感资产信息监控脚本:员工 https://github.com/x0day/Multisearch-v2 (Bing、google、360、zoomeye等搜索引擎聚合搜索,可用于发现企业被搜索引擎收录的敏感资产信息) https://github.com/Ekultek/Zeus-Scanner (集成化的综合搜索引擎,能够抓取被搜索引擎隐藏的url,并交由sqlmap、nmap扫描) https://github.com/0xbug/Biu-framework (企业内网基础服务安全扫描框架) https://github.com/metac0rtex/GitHarvester (github Repo信息搜集工具) https://github.com/shengqi158/svnhack (.svn文件夹泄漏利用工具) https://github.com/repoog/GitPrey (GitHub敏感信息扫描工具) https://github.com/0xbug/Hawkeye (企业资产、敏感信息GitHub泄露监控系统) https://github.com/lianfeng30/githubscan (根据企业关键词进行项目检索以及相应敏感文件和文件内容扫描的工具) https://github.com/UnkL4b/GitMiner (github敏感信息搜索工具) https://github.com/lijiejie/GitHack (.git文件夹泄漏利用工具) https://github.com/dxa4481/truffleHog (GitHub敏感信息扫描工具,包括检测commit等) https://github.com/sowish/LNScan (详细的内部网络信息扫描器) https://github.com/SkyLined/LocalNetworkScanner (javascript实现的本地网络扫描器) https://github.com/x0day/Multisearch-v2 (搜索引擎聚合搜索,可用于发现企业被搜索引擎收录的敏感资产信息) webshell检测或病毒分析工具 https://github.com/ym2011/ScanBackdoor (一款简洁的Webshell扫描工具) https://github.com/yassineaddi/BackdoorMan (可对指定目录进行php webshell检测) https://github.com/he1m4n6a/findWebshell (一款简单的webshell检测工具) https://github.com/Tencent/HaboMalHunter (哈勃分析系统,linux系统病毒分析及安全检测) https://github.com/PlagueScanner/PlagueScanner (使用python实现的集成ClamAV、ESET、Bitdefender的反病毒引擎) https://github.com/nbs-system/php-malware-finder (一款高效率PHP-webshell扫描工具) https://github.com/emposha/PHP-Shell-Detector/ (测试效率高达99%的webshell检测工具) https://github.com/erevus-cn/scan_webshell (一款简洁的Webshell扫描工具) https://github.com/emposha/Shell-Detector (Webshell扫描工具,支持php/perl/asp/aspx webshell扫描) https://github.com/m4rco-/dorothy2 (一款木马、僵尸网络分析框架) 内网渗透或扫描工具 https://github.com/0xwindows/VulScritp (企业内网渗透脚本,包括banner扫描、端口扫描;phpmyadmin、jenkins等通用漏洞利用等) https://github.com/lcatro/network_backdoor_scanner (基于网络流量的内网探测框架) https://github.com/fdiskyou/hunter (调用 Windows API 枚举用户登录信息) https://github.com/BlackHole1/WebRtcXSS (自动化利用XSS入侵内网) https://github.com/0xwindows/VulScritp (企业内网渗透脚本,包括banner扫描、端口扫描;各种通用漏洞利用等) https://github.com/fdiskyou/hunter (调用 Windows API 枚举用户登录信息) https://github.com/AlessandroZ/LaZagne (本机密码查看提取工具) https://github.com/huntergregal/mimipenguin (linux密码抓取神器) 中间件扫描器或识别工具 https://nmap.org/download.html (Nmap端口扫描器之王,- https://svn.nmap.org/) https://github.com/ring04h/wyportmap (目标端口扫描+系统服务指纹识别) https://github.com/ring04h/weakfilescan (动态多线程敏感信息泄露检测工具) https://github.com/EnableSecurity/wafw00f (WAF产品指纹识别) https://github.com/rbsec/sslscan (ssl类型识别) https://github.com/urbanadventurer/whatweb (web指纹识别) https://github.com/tanjiti/FingerPrint (web应用指纹识别) https://github.com/nanshihui/Scan-T (网络爬虫式指纹识别) https://github.com/OffensivePython/Nscan (a fast Network scanner inspired by Masscan and Zmap) https://github.com/ywolf/F-NAScan (网络资产信息扫描, ICMP存活探测,端口扫描,端口指纹服务识别) https://github.com/ywolf/F-MiddlewareScan (中间件扫描) https://github.com/maurosoria/dirsearch (Web path scanner) https://github.com/x0day/bannerscan (C段Banner与路径扫描) https://github.com/RASSec/RASscan (端口服务扫描) https://github.com/3xp10it/bypass_waf (waf自动暴破) https://github.com/3xp10it/xcdn (尝试找出cdn背后的真实ip) https://github.com/Xyntax/BingC (基于Bing搜索引擎的C段/旁站查询,多线程,支持API) https://github.com/Xyntax/DirBrute (多线程WEB目录爆破工具) https://github.com/zer0h/- httpscan (一个爬虫式的网段Web主机发现小工具) https://github.com/lietdai/doom (thorn上实现的分布式任务分发的ip端口漏洞扫描器) https://github.com/chichou/grab.js (类似 zgrab 的快速 TCP 指纹抓取解析工具,支持更多协议) https://github.com/Nitr4x/whichCDN (CDN识别、检测) https://github.com/secfree/bcrpscan (基于爬虫的web路径扫描器) https://github.com/ring04h/wyportmap (目标端口扫描+系统服务指纹识别) https://github.com/rbsec/sslscan (SSL类型识别) https://github.com/urbanadventurer/whatweb (Web指纹识别) https://github.com/tanjiti/FingerPrint (Web应用指纹识别) https://github.com/OffensivePython/Nscan (基于Masscan和Zmap的网络扫描器) https://github.com/maurosoria/dirsearch (web路径收集与扫描) https://github.com/3xp10it/xcdn (尝试找出cdn背后的真实ip) https://github.com/lietdai/doom (Thorn上实现的分布式任务分发的ip端口漏洞扫描器) https://github.com/mozilla/ssh_scan (服务器ssh配置信息扫描) https://github.com/18F/domain-scan (针对域名及其子域名的资产数据检测/扫描,包括- http/- https检测等) https://github.com/ggusoft/inforfinder (域名资产收集及指纹识别工具) https://github.com/boy-hack/gwhatweb (CMS识别 python gevent实现) https://github.com/Mosuan/FileScan (敏感文件扫描 / 二次判断降低误报率 / 扫描内容规则化 / 多目录扫描) https://github.com/Xyntax/FileSensor (基于爬虫的动态敏感文件探测工具) https://github.com/deibit/cansina (web路径扫描工具) https://github.com/0xbug/Howl (网络设备 web 服务指纹扫描与检索) https://github.com/mozilla/cipherscan (目标主机服务ssl类型识别) https://github.com/xmendez/wfuzz (Web应用fuzz工具、框架,同时可用于web路径/服务扫描) https://github.com/UltimateHackers/Breacher (多线程的后台路径扫描器,也可用于发现Execution After Redirect漏洞) https://github.com/ztgrace/changeme (弱口令扫描器,不仅支持普通登录页,也支持ssh、mongodb等组件) https://github.com/medbenali/CyberScan (渗透测试辅助工具,支持分析数据包、解码、端口扫描、IP地址分析等) https://github.com/m0nad/HellRaiser (基于nmap的扫描器,与cve漏洞关联) https://github.com/scipag/vulscan (基于nmap的高级漏洞扫描器,命令行环境使用) https://github.com/jekyc/wig (web应用信息搜集工具) https://github.com/eldraco/domain_analyzer (围绕web服务的域名进行信息收集和"域传送"等漏洞扫描,也支持针对背后的服务器端口扫描等) https://github.com/cloudtracer/paskto (基于Nikto扫描规则的被动式路径扫描以及信息爬虫) https://github.com/zerokeeper/WebEye (快速识别WEB服务器类型、CMS类型、WAF类型、WHOIS信息、以及语言框架) https://github.com/m3liot/shcheck (用于检查web服务的- http header的安全性) https://github.com/aipengjie/sensitivefilescan (一款高效快捷的敏感文件扫描工具) https://github.com/fnk0c/cangibrina (通过字典穷举、google、robots.txt等途径的跨平台后台管理路径扫描器) https://github.com/n4xh4ck5/CMSsc4n (CMS指纹识别) 专用(即特定性针对某些组件)扫描器 https://github.com/brianwrf/hackUtils (java反序列化利用工具集) https://github.com/frohoff/ysoserial ( java反序列化利用工具) https://github.com/blackye/Jenkins (Jenkins漏洞探测、用户抓取爆破) https://github.com/code-scan/dzscan (discuz漏洞扫描) https://github.com/chuhades/CMS-Exploit-Framework (CMS攻击框架) https://github.com/lijiejie/IIS_shortname_Scanner (IIS短文件名漏洞扫描) https://github.com/riusksk/FlashScanner (flashxss扫描) https://github.com/coffeehb/SSTIF (服务器端模板注入漏洞的半自动化工具) https://github.com/epinna/tplmap (服务器端模板注入漏洞检测与利用工具) https://github.com/cr0hn/dockerscan (docker扫描工具) https://github.com/GoSecure/break-fast-serial (借助DNS解析来检测Java反序列化漏洞工具) https://github.com/dirtycow/dirtycow.github.io (脏牛提权漏洞exp) https://github.com/code-scan/dzscan (首款集成化的Discuz扫描工具) https://github.com/chuhades/CMS-Exploit-Framework (一款简洁优雅的CMS扫描利用框架) https://github.com/lijiejie/IIS_shortname_Scanner (IIS短文件名暴力枚举漏洞利用工具) https://github.com/coffeehb/SSTIF (一个Fuzzing服务器端模板注入漏洞的半自动化工具) https://github.com/cr0hn/dockerscan (Docker扫描工具) https://github.com/m4ll0k/WPSeku (一款精简的wordpress扫描工具) https://github.com/rastating/wordpress-exploit-framework (集成化wordpress漏洞利用框架) https://github.com/ilmila/J2EEScan (用于扫描J2EE应用的一款burpsuite插件) https://github.com/riusksk/StrutScan (一款基于perl的strut2的历史漏洞扫描器) https://github.com/D35m0nd142/LFISuite (本地文件包含漏洞利用及扫描工具,支持反弹shell) https://github.com/0x4D31/salt-scanner (基于Salt Open以及Vulners Linux Audit API的linux漏洞扫描器,支持与JIRA、slack平台结合使用) https://github.com/tijme/angularjs-csti-scanner (自动化探测客户端AngularJS模板注入漏洞工具) https://github.com/irsdl/IIS-ShortName-Scanner (Java编写的IIS短文件名暴力枚举漏洞利用工具) https://github.com/swisskyrepo/Wordpresscan (基于WPScan以及WPSeku的优化版wordpress扫描器) https://github.com/CHYbeta/cmsPoc (CMS渗透测试框架) https://github.com/rudSarkar/crlf-injector (CRLF注入漏洞批量扫描) https://github.com/3gstudent/Smbtouch-Scanner (自动化扫描内网中存在的由shadow brokers泄露的ETERNAL系列漏洞) https://github.com/utiso/dorkbot (通过定制化的谷歌搜索引擎进行漏洞页面搜寻及扫描) https://github.com/OsandaMalith/LFiFreak (本地文件包含漏洞利用及扫描工具,支持反弹shell) https://github.com/mak-/parameth (用于枚举脚本的GET/POST未知参数字段) https://github.com/Lucifer1993/struts-scan (struts2漏洞全版本检测和利用工具) https://github.com/hahwul/a2sv (SSL漏洞扫描,例如心脏滴血漏洞等) https://github.com/NullArray/DorkNet (基于搜索引擎的漏洞网页搜寻) https://github.com/NickstaDB/BaRMIe (用于攻击爆破Java Remote Method Invocation服务的工具) https://github.com/RetireJS/grunt-retire (扫描js扩展库的常见漏洞) https://github.com/kotobukki/BDA (针对hadoop/spark等大数据平台的的漏洞探测工具) https://github.com/jagracey/Regex-DoS (RegEx 拒绝服务扫描器) https://github.com/milesrichardson/docker-onion-nmap (使用nmap扫描Tor网络上隐藏的"onion"服务) https://github.com/Moham3dRiahi/XAttacker (Web CMS Exploit 工具,包含针对主流 CMS 的 66 个不同的 Exploits) https://github.com/lijiejie/BBScan (一个迷你的信息泄漏批量扫描脚本) 无线网络(审计)扫描器 https://github.com/savio-code/fern-wifi-cracker/ (无线安全审计工具) https://github.com/m4n3dw0lf/PytheM (Python网络/渗透测试工具) https://github.com/P0cL4bs/WiFi-Pumpkin (无线安全渗透测试套件) https://github.com/MisterBianco/BoopSuite (无线网络审计工具,支持2-5GHZ频段) https://github.com/DanMcInerney/LANs.py (ARP欺骗,无线网络劫持) https://github.com/besimaltnok/PiFinger (检查wifi是否是"大菠萝"所开放的热点,并给予网络评分) https://github.com/derv82/wifite2 (自动化无线网络攻击工具wifite的重构版本) 局域网络(本地网络)扫描器 https://github.com/sowish/LNScan (基于BBScan via.lijiejie的本地网络扫描) https://github.com/niloofarkheirkhah/nili (网络扫描,中间人攻击,协议检测与逆向) https://github.com/SkyLined/LocalNetworkScanner (基于javascript的本地网络扫描) 代码审计工具或扫描器 https://github.com/wufeifei/cobra (白盒代码安全审计系统) https://github.com/OneSourceCat/phpvulhunter (静态php代码审计) https://github.com/Qihoo360/phptrace (跟踪、分析PHP运行情况的工具) https://github.com/ajinabraham/NodeJsScan (NodeJS应用代码审计) https://github.com/shengqi158/pyvulhunter (Python应用审计) https://github.com/presidentbeef/brakeman ( Ruby on ... 综合来看,fuzzdb-collect在同类工具中还是有一定优势的,特别是在功能完整性和易用性方面表现不错。如果你有相关需求,可以下载试试。 {card-default label="? 工具信息" /} ? 工具名称:fuzzdb-collect ? 开发作者:euphratica ? 工具描述:网络上安全资源的搜集 ? 开发语言:Python ? 开源协议:未知开源协议 ⭐ Star数:2 | ? Fork数:1 ? 更新时间:2026年08月06日 {/card-default} {cloud type="default" title="网盘下载" url="https://gitee.com/euphratica/fuzzdb-collect/repository/archive/master.zip"} {cloud type="default" title="网盘下载" url="https://gitee.com/euphratica/fuzzdb-collect.git"}


