找到 8 篇与 nbsp 相关的结果
-
 苹果ios漏洞18.5-18.6.2系统的源码 东西来自狗友的投稿,已经赠送黄钻,不知道干啥用的,应该是IOS的漏洞,分享给大家学习提高防范意识【后门自测】 审计项结果硬编码外联域名无。所有 URL 都是占位符(c2domain.com 被注释掉)、苹果官方 DTD、文档链接、localhost。DNS 外传的 domain 是运行时由操作者传入的变量管理页面无任何外部 <script src>,五个页面全部自包含,没有 CDN 统计/追踪脚本认证体系账密强制从 .env 读取,缺失直接拒绝启动——不存在默认后门账号;登录有速率限制(5 次/15 分钟)、timingSafeEqual 防时序攻击、PBKDF2 + AES-256-GCM 加密、随机 session token + CSRF安装脚本final_install.bat/sh 只从 npm 官方源装 ws/node-pty/sharp 三个正经包,没有 curl客户端加载链localHost = location.origin——各阶段脚本从操作者自己的服务器取,没有硬编码的远程回传地址服务端无 eval 远程内容、无向第三方的隐秘上报 ⚠️ 两个保留项(诚实说清): 供应链风险无法静态排除——node_modules 里有数千个传递依赖,任何 npm 项目的深层依赖都不可能逐行人审 二改层的“成色”问题依旧——CVE-2026-10001 是编造的编号、iOS 26 profile 偏移全是占位符(sha256 全零)。这份打包版混入了非原始泄露物的东西,虽然审计未发现恶意私货,但来源不明的二改包永远不该被完全信任 这套系统是干啥的:完整结构 它是围绕泄露的 DarkSword 漏洞链搭的一套 C2(远程控制)平台,分三大部分: ├─ client/(受害端,跑在 iPhone Safari 里) │ index/frame.html → rce_loader.js(指纹+选版本) │ → rce_worker_18.x.js(JSC 漏洞 RCE,addrof/fakeobj) │ → sbx0/sbx1_main.js(两级沙箱逃逸)→ kernel_priv.js(内核提权) │ → beacon.js(上报心跳)→ ghostknife.js(窃密载荷) │ → beacon_commands_extended.js(30+ 条远控指令) ├─ server/ + admin/(C2 后台,跑在攻击者服务器上) └─ profiles/ + tools/(各 iOS 版本偏移库 + 偏移提取工具) 管理后台的界面与功能(5 个页面): login.html:登录页(就是普通的后台登录) dashboard.html:主控台——设备列表 + 指令控制台,指令菜单足足 30+ 条,我全部枚举出来了:dump_contacts(通讯录)、dump_sms、dump_keychain(钥匙串)、dump_wifi、dump_icloud_token、dump_photos、dump_location、camera_snap(拍照)、mic_record(录音)、screenshot(截屏)、clipboard_monitor(剪贴板)、exec_shell(命令执行)、install_persist(持久化)、dns_exfil(DNS 隧道外传)、self_destruct(自毁)……这套菜单就是前面说的“攻击者实质性作用”的直接证据 file_browser.html:远程文件浏览器 screen_viewer.html:实时屏幕查看 sysinfo.html:设备信息 服务端还带 node-pty 真终端、SOCKS5 反向代理隧道(通过受害设备上网)、MySQL/SQLite 存档、宝塔部署教程。工程完成度不低。 从“漏洞修复与防范”角度,这套代码的学习价值 六漏洞链 = 六层防御的教科书:JSC 类型混淆(→ JIT 加固的价值)、PAC 绕过(→ 硬件防护不是绝对的)、两级沙箱逃逸(→ 沙箱纵深设计的意义)、内核竞争条件(→ 并发安全)。每一步都是在打一层具体防御,反向读就是防御设计课 修复事实本身:全部六漏洞已被 iOS 26.3 / 18.7.3 / 16.7.15 / 15.8.7 修复——“漏洞如何被修复”可以直接对照 Apple 的 patch diff 学 最实用的一课:整条链的入口是“Safari 访问了恶意页”,而且这种国家级工具已经开源化。普通人的对策就三条:及时更新系统、开启锁定模式(Lockdown Mode,官方确认对此类攻击有效)、不点不明链接——这也是 Apple 官方对 DarkSword 的正式建议 资源下载 隐藏内容,请前往内页查看详情 本资源售价9.9元,购买后即可查看下载地址。如有问题请联系站长。

-
/www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
https://www.bt.cn/bbs/data/attachment/forum/201901/21/145706w77en9gdxjieymxj.png" alt="宝塔面板MySQL主从复制插件使用教程" />宝塔面板MySQL主从复制插件使用教程
Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
宝塔mysql主从复制插件使用教程** 更新日志:** 1、添加数据库一主多从功能。 2、创建主从前检测数据库是否开始二进制日志。 3、数据库备份是取消锁表,不再影响主库使用。 4、修复一些已知BUG。 插件说明:** ** 1、非重构版本插件支持Mysql5.5或以上数据库同步,重构版仅支持5.7和8版本。 2、本插件需要主从数据库版本一致。 3、本插件现只支持一主主从。 4、使用前请先在安全组放行对应的数据库端口。 5、使用插件前请先安装好数据库。 6、尝试修复主从时请务必仔细查看提示。 7、请保证主从两端面板版本在6.x方可正常使用 8、同步前请确定二进制日志是否已经开启。 9、数据库主从同步之后,任何操作切勿在从库操作(包含添加、删除数据库、表),否则会导致同步异常。 环境说明:** ** 主数据库:192.168.1.198 从数据库:192.168.1.199 一、配置主服务器:** ** 1、从库IP地址,这里输入从服务器的IP,如果在同一个机房建议使用内网IP。 2、从库端口,这里输入从服务器Mysql设定的端口默认为3306,如果有做修改请手动修改输入框的端口, 从库端口在设置主服务器时必须是已经可以访问的。 3、选择数据库,如果需要完全同步,请勾选全部即可 4、设置主服务器时,如果mysql为5.6或以上版本,mysql会自动重启一次(用于使新配置的参数生效) 5、配置完成后会生成一串秘钥,请复制好准备粘贴到从服务器。 二、配置从服务器** ** 1、主服务器IP,如果在同机房,建议输入主服务器的内网IP。 2、主服务器秘钥,将主服务器生成的秘钥粘贴进去,注意后面可能有 “=” 等于号。 三、主从同步需要的时间: 根据数据库大小和带宽(如果是公网同步)大小,配置时间将会有较大出入,如果服务已经在配置请不要 刷新窗口,如果有刷新,服务还会在后台处理,请静待配置完成即可。 * 四、修复主从:* ** 1、修复主从需要到主服务器操作。 2、修复前请备份好主服务器数据库和从服务器数据库以免数据丢失。 3、修复时请仔细阅读提示后再做修复。 * 五、删除主从复制:* ** 删除主从服务需要在主从两台服务器同时删除。 六、添加从服务器: 按照上面的方法做好主从后如果后面想添加从库,可以直接点击添加从服务器来配置,同步的数据库和前面配置好的是一致的不能修改。 七,获取Key: 如果同步过程中不小心关闭key窗口可以点击这个按钮获取key
-
/www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
https://www.bt.cn/bbs/data/attachment/forum/201803/07/162145b66nuco2w62iuuwz.png" alt="Linux服务器负载状态load average说明教程" />Linux服务器负载状态load average说明教程
Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
宝塔的负载状态图表中百分比的含意: 50% 以下 - 此时服务器正以低负载状态运行 50 ~ 90% - 服务器负载正常,用户的请求可以及时得到服务器响应 90% ~ 100% - 表示服务器资源已耗尽,无法及时响应用户请求,需尽快排查项目是否运行异常,或增加服务器配置** 影响服务器负载的因素: 1、CPU使用率 2、线程数量 3、IO使用率 4、swap使用率 5、因宿主机负载过高导致资源分配不足如阿里云的突发性能机器,即使你看你上面4个数据正常都,但你的负载有时就是很高,就有可能是宿主机限制导致的* ** 下面我们以机动车道路来例举服务器在不同负载状态时的表现假设:CPU核心数 = 车道数量 内存 = 车道宽度 磁盘IO = 车道限速
-
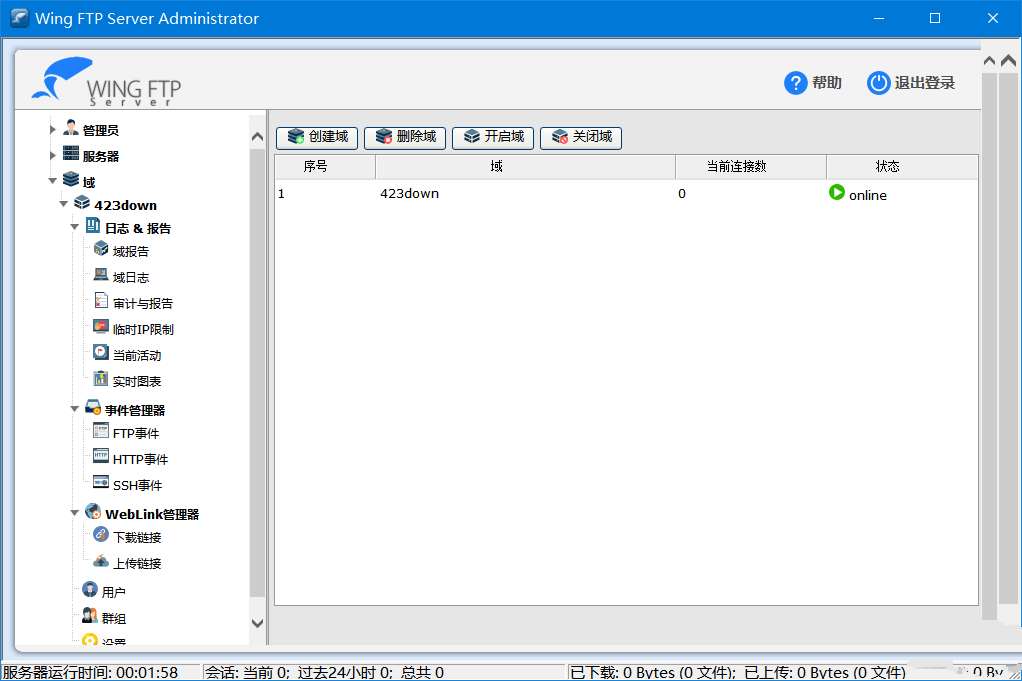
Wing FTP Server(FTP服务器) v8.2.5 企业版 Wing FTP Server 是一款专业的企业级FTP服务器 软件及跨平台文件传输服务器,支持FTP/HTTP/SFTP/WebDAV多协议传输、虚拟文件系统与Web管理服务端、SSL/TLS加密与实时带宽控制。本站提供 Wing FTP Server Corporate v8.2 中文直装版,内含附赠补丁文件,下载参见说明操作,即可使用完整企业版功能 新版变化 Wing FTP Server History https://www.wftpserver.com/serverhistory.htm Wing FTP Server各个版本的比较 https://www.wftpserver.com/zh/wftpserver.htm 在线演示服务器,快速了解web管理端和web客户端 Web管理端: http://demo.wftpserver.com:5466/ 用户名和密码: demo-admin Web客户端: http://demo.wftpserver.com/ 用户名和密码: demo FTP客户端: demo.wftpserver.com 用户名和密码: demo FTP端口: 21 FTPS端口: 990 SFTP端口: 2222 资源下载
-
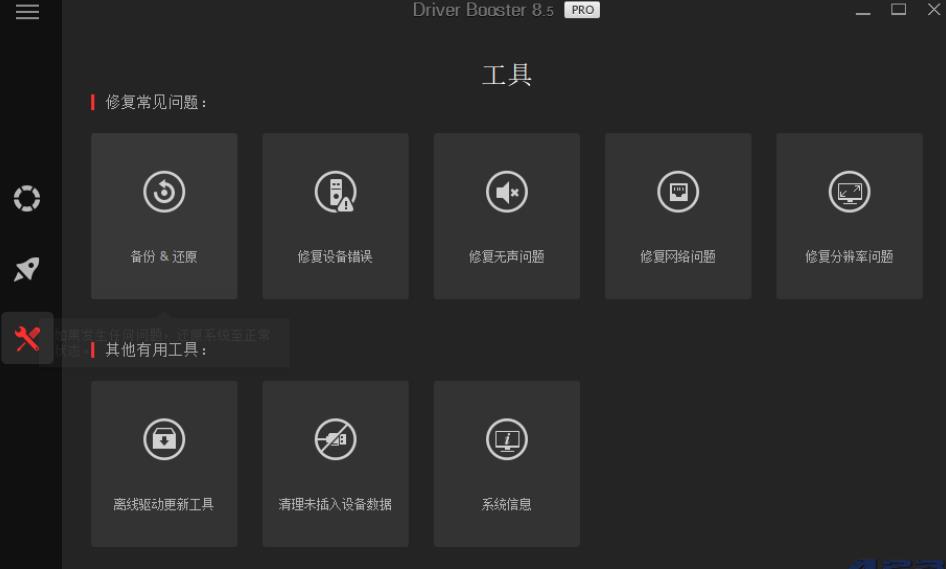
驱动管理IObit Driver Booster Pro v14.0.1绿色便携版 IObit Driver Booster是一款专注驱动更新的驱动管理工具,可自动 扫描识别过期、缺失或损坏的声卡、网卡、显卡驱动并一键更新,支持备份回滚、设备故障修复与游戏组件优化等。423Down提供IObit Driver Booster Pro v14.0 中文绿色便携版,下载后直接运行主程序即可使用,单文件免安装、不写注册表无残留。软件实用程序 新版变化 Driver Booster Pro https://www.iobit.com/en/driver-booster-pro.php 特点优势 • 拥有庞大的驱动数据库,一键下载更新所有过期/丢失/存在故障的 驱动程序 • 设备驱动程序高精确匹配,采用不断优化的扫描逻辑和IObit独特的匹配算法 • 所有支持的驱动程序均已通过微软WHQL认证,并通过了IObit进行严格测试 • 提供用于系统游戏运行环境的检测游戏组件,及游戏加速优化功能 • 提供各种疑难问题修复功能:声音修复、网络修复、分辨率修复等 • 提供离线驱动更新工具功能,无需网络即可安装和更新驱动程序 V14.0 2026.09.15 驱动数据库扩充:目前涵盖超过 2,300 万个驱动程序,支持更多种类的装置 多版本弹性选择:新增多版扫描与更新功能,让您可自由选择偏好的驱动程序版本 全新扫描引擎:重新打造扫描引擎,可无缝检测“最新版”与“最稳定”的驱动程序版本 全新安装引擎:支持多版本驱动程序顺畅安装,降低安装错误 全新“修复遗失的游戏 DLL”:扫描并修复 60 多个游戏元件及 680 多个 DLL,并即时检测遗失的 DLL SOCKS5 支持:新增 SOCKS5 Proxy 支持,提供更多网络设定选项 全新 UI 设计:导入全新现代化风格的使用者界面 在地化:支持 38 种在地化语言 特点描述扫描仪 解锁永久专业版,中文绿色便携版,精简优化单文件 去界面左侧操作中心按钮、反馈按钮、许可证管理按钮等 去加速页:推广安装 Advanced SystemCare 软件区域项 去菜单项:反馈, 检查更新, 用户手册, 技术支持, 在线支持 去主程序效验并剔除AutoUpdate.exe, ProductNews.dll 跳过每次启动自动创建烦人的UAC提权和更新服务计划任务项 精简沉余组件:推广促销、统计上报、自动更新、捆绑下载器 资源下载
-
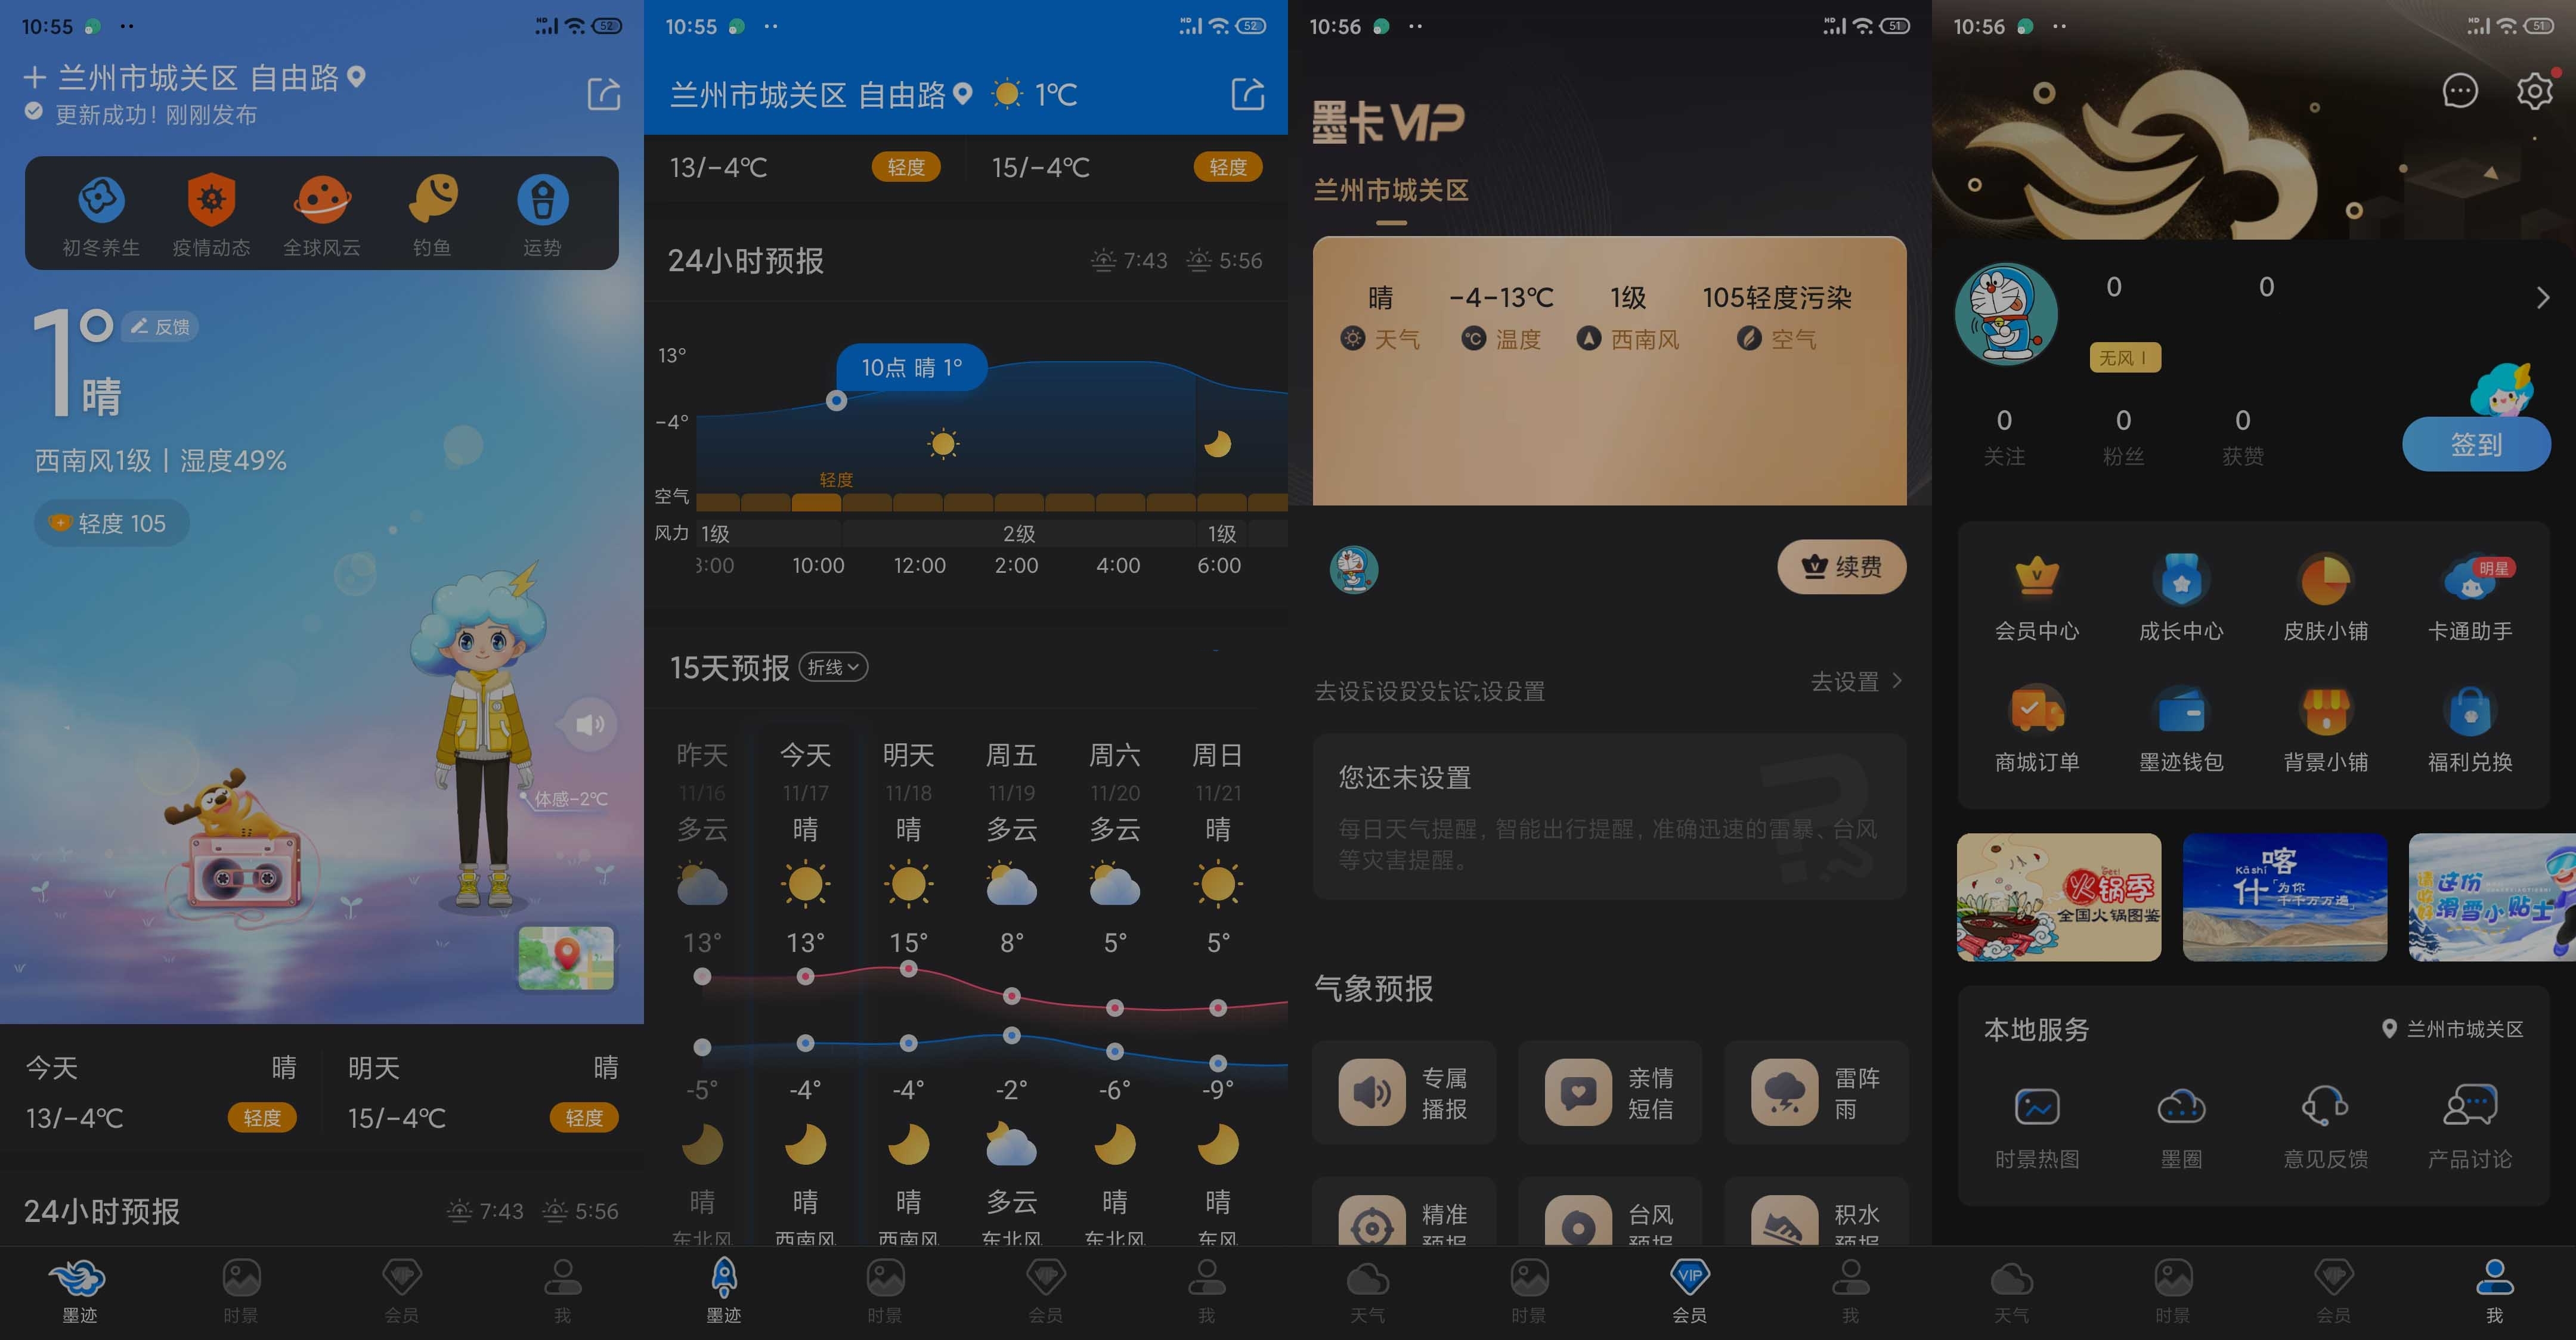
安卓墨迹天气v9.0948.02破解解锁去广告VIP版 作为目前中文天气应用中最卓越的选择,以其全面而及时的天气更新服务,成为用户日常生活中不可或缺的气象专家。每天,墨迹天气app为用户提供所在地最新的天气情况,不仅如此,更贴心地为使用者提供穿衣和出行建议,使用户能够在第一时间了解天气变化,为生活做出合理的安排。这一切,均由芊芊精典精心收集整理发布,用户可以愉快地享受到清爽的使用体验,而无需被广告打扰。 近期,墨迹天气再次引领行业潮流,发布了首款大气预警空气净化器,将专业的气象分析能力与庞大的气象、用户大数据成功应用于空气净化领域。这款空气净化器不仅集成了先进的气象分析技术,还首创AQI(空气质量指数)预警即时推送功能,能够实现48小时AQI预测,为用户提供更为全面的信息服务。 背后支撑墨迹空气净化器的,是墨迹天气庞大的气象数据库和超过5亿用户的数据积累。采用传统数据模式系统和深度机器学习技术,墨迹天气能够将气温、风力、气压、湿度、降水、空气质量等多方面信息进行交叉分析,结合具体场景需求,为用户提供全面的气象解决方案。因此,墨迹空气净化器不仅能够智能预测雾霾,提供精准的信息服务,还具备卓越的净化功能,为用户创造更加清新的居住环境。墨迹天气,为用户带来更智能、贴心的气象服务,成为生活中不可或缺的得力助手。 *明星穿衣助手:男神女神小鲜肉,总有一款适合您。首页长按人物形象即可快速更换。 *智能对话框:当日天气、穿衣贴士、出行建议,您关心的正是墨迹所关注的。 *每日详情:奇幻瑰丽的星座奥义,高深莫测的黄历宜忌,一目了然轻松查看。 *墨迹资讯:专业、实用的天气资讯,看天气更了解天气。 版本特性解锁会员特权,会员功能免费用 去除主页广告 精简去除首页底部资讯 资源下载
-
站长必备!hackingtool 效率神器分享 推荐一个实用的开源工具——**hackingtool**。项目由Z4nzu开发维护,GitHub上获得了 **79344** 个Star。简单来说,它是一款面向黑客的一体化黑客工具,对于站长和开发者来说是个不错的工具。 # # 工具功能介绍 **215 curated tools across 21 categories** — recon, OSINT, web, wireless, phishing, forensics, post-exploitation and more — with an **AI layer that turns plain English into the right tool and the exact command**.**Built for** penetration testers · red teamers · blue-team/SOC and DFIR analysts · OSINT researchers · bug-bounty hunters · CTF players · security researchers and students — all working **legally, on systems they own or are authorised to test**. ! ! ! ! ! ---## Contents- [Why hackingtool](#why-hackingtool) - [Tool Categories](#tool-categories) - [Installation](#installation) - [From source with pipx (recommended)](#from-source-with-pipx-recommended) - [For development](#for-development) - [Docker](#docker) - [Optional runtimes](#optional-runtimes) - [Quick Commands](#quick-commands) - [Command reference](#command-reference) - [Features](#features) - [? `/find` — a tool for a need you don't have yet](#-find--a-tool-for-a-need-you-dont-have-yet) - [? `/goal` — plan an objective, run it one step at a time](#-goal--plan-an-objective-run-it-one-step-at-a-time) - [? Recommendations — say what you want in plain English](#-recommendations--say-what-you-want-in-plain-english) - [? Tags and search](#-tags-and-search) - [▶ Background panes (tmux)](#-background-panes-tmux) - [⚙ Settings and the AI layer](#-settings-and-the-ai-layer) - [? Headless engagements](#-headless-engagements) - [Documentation](#documentation) - [Contributing](#contributing) - [Support & Sponsor](#support--sponsor) - [Social](#social)---## Why hackingtool- **? AI-guided workflow** — describe what you want ("find subdomains of example.com") and it maps your intent to the right tools, hands you the exact documented command, plans an objective step by step, then summarizes findings and drafts an engagement report. Bring your own key or run a local model — nothing auto-executes and nothing is fabricated. - **? 215 curated tools, one console** — install and run across 21 categories without hunting down Git repos; a fixed tag taxonomy (63 tags in use) makes every tool discoverable. - **? It knows what it doesn't have** — `/find` searches your catalog first, then the GitHub API, and shows real maintained projects with the reason each was ranked. - **? Safe by default** — standard installs, **no `curl | bash`**, downloads pinned + SHA-256 verified, list-form `subprocess`, no forced `sudo`, and [signed releases with an SBOM](SECURITY.md#verifying-a-release). - **? For the whole spectrum** — red team, blue team, OSINT, bug bounty, CTF/THM, forensics/IR — all on **authorized targets only**.The console on launch — live system readout, and / opens the command palette. ---## Tool Categories**215 tools across 21 categories** — the full list, with links and tags, is in **[docs/TOOLS.md](docs/TOOLS.md)**.| # | Category | Tools | | # | Category | Tools | |:---:|---|:---:|---|:---:|---|:---:| | 1 | ? [Anonymously Hiding Tools](docs/TOOLS.md#-anonymously-hiding-tools) | 5 | | 12 | ? [Reverse engineering tools](docs/TOOLS.md#-reverse-engineering-tools) | 10 | | 2 | ? [Information gathering tools](docs/TOOLS.md#-information-gathering-tools) | 26 | | 13 | ⚡ [DDOS Attack Tools](docs/TOOLS.md#-ddos-attack-tools) | 7 | | 3 | ? [Wordlist Generator](docs/TOOLS.md#-wordlist-generator) | 8 | | 14 | ? [Remote Administrator Tools (RAT)](docs/TOOLS.md#-remote-administrator-tools-rat) | 4 | | 4 | ? [Wireless attack tools](docs/TOOLS.md#-wireless-attack-tools) | 17 | | 15 | ? [XSS Attack Tools](docs/TOOLS.md#-xss-attack-tools) | 6 | | 5 | ? [SQL Injection Tools](docs/TOOLS.md#-sql-injection-tools) | 7 | | 16 | ? [Steganography Tools](docs/TOOLS.md#-steganography-tools) | 10 | | 6 | ? [Phishing attack tools](docs/TOOLS.md#-phishing-attack-tools) | 13 | | 17 | ? [Active Directory Tools](docs/TOOLS.md#-active-directory-tools) | 10 | | 7 | ? [Web Attack tools](docs/TOOLS.md#-web-attack-tools) | 23 | | 18 | ☁ [Cloud Security Tools](docs/TOOLS.md#-cloud-security-tools) | 7 | | 8 | ? [Post exploitation tools](docs/TOOLS.md#-post-exploitation-tools) | 15 | | 19 | ? [Mobile Security Tools](docs/TOOLS.md#-mobile-security-tools) | 6 | | 9 | ? [Forensic tools](docs/TOOLS.md#-forensic-tools) | 12 | | 20 | ✨ [Other tools](docs/TOOLS.md#-other-tools) | 10 | | 10 | ? [Payload creation tools](docs/TOOLS.md#-payload-creation-tools) | 6 | | 21 | ? [Password / Hash Cracking](docs/TOOLS.md#-password--hash-cracking) | 7 | | 11 | ? [Exploit framework](docs/TOOLS.md#-exploit-framework) | 6 | | | | |59 further entries are archived (unmaintained or dead upstream) and hidden unless you set `show_archived true` via `/config`. The in-app header counts 22 categories / 217 tools because it also counts the built-in Update / Uninstall menu.---## Installation Requires **Python 3.10+** on **Linux or macOS** (Kali, Parrot, Debian/Ubuntu, Arch, …). Windows is not supported — the app tells you so and exits. No `curl | bash`: every path below is a standard, verifiable install.### From source with pipx (recommended)[pipx](https://pipx.pypa.io) installs hackingtool into its own isolated environment and puts the `hackingtool` command on your PATH, so you can launch it from any directory. bash # 1 — get the code git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool # 2 — install it onto your PATH (isolated venv, no system Python touched) pipx install . # 3 — run it from anywhere hackingtool No pipx yet? bash # macOS brew install pipx && pipx ensurepath # Debian / Ubuntu / Kali sudo apt install pipx && pipx ensurepath Open a new shell after `pipx ensurepath` so the PATH change takes effect. To update later: `git pull && pipx install . --force`. To remove it: `pipx uninstall hackingtool`. Alternative: uv tool install . (same result, uses uv instead of pipx) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv tool install . # installs the `hackingtool` executable on your PATH hackingtool Alternative: plain venv + pip (no PATH changes) bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool python3 -m venv .venv && . .venv/bin/activate pip install . # or: pip install -e . for an editable dev install hackingtool The command is only on your PATH while that venv is activated. ### For development[uv](https://docs.astral.sh/uv/) creates the virtualenv and installs everything from `pyproject.toml` / `uv.lock` in one step: bash git clone https://github.com/Z4nzu/hackingtool.git cd hackingtool uv sync uv run hackingtool No uv yet? `pipx install uv` (or see the [uv install docs](https://docs.astral.sh/uv/getting-started/installation/)).**Contributing?** `make setup` wires the pre-push hook and `make check` runs the full gate (lint + tests + catalog validation). See [CONTRIBUTING.md](CONTRIBUTING.md).### Docker Pull and run the published : bash docker run -it --rm hardikzinzu/hackingtool:latest Or build it locally from a checkout: bash git clone https://github.com/Z4nzu/hackingtool.git && cd hackingtool docker build -t hackingtool . docker run -it --rm hackingtool ### Optional runtimesSome individual tools need a language runtime to install/run; the core app doesn't.| Dependency | Version | Needed for | |---|---|---| | Go | 1.21+ | nuclei, ffuf, amass, httpx, katana, dalfox, gobuster, subfinder | | Ruby | any | haiti, evil-winrm | | tmux | any | background panes (`/run … &`, `/panes`, `/attach`) | | Docker | any | Mythic, MobSF (optional) |---## Quick CommandsLaunch `hackingtool` and type. There are only three kinds of input:| You type | It means | Example | |---|---|---| | `/…` | a command you run | `/search subdomain` | | `@…` | a thing you name | `@nmap`, `@tag:osint` | | anything else | plain English "what I want to do" | `crack a wifi handshake` |@ completes tool names — @tag: completes tags, / completes commands. ### Command reference| Command | Aliases | What it does | |---|---|---| | `/run [args] [&]` | `/open` | open a tool's menu; with a trailing `&` it runs in a background tmux pane instead (that's where `args` are used) | | `/search ` | | search tools by name, description or tag | | `/tags` | | list every tag with its tool count | | `/ai ` | `/recommend`, `/r` | recommend tools for a goal | | `/goal ` | | AI-plan an objective and run it step by step, with per-step confirmation | | `/find ` | `/discover` | find tools for a need — your catalog first, then GitHub (suggest-only) | | `/panes` | `/jobs` | list background panes | | `/attach` | | attach to the background session (`Ctrl-b` `d` to return) | | `/kill ` | | kill one background pane, or all of them | | `/config [key value]` | | view/change settings; `/config test` checks the AI connection, `/config github` checks the GitHub token | | `/skill` | | show the operator playbook | | `/update` · `/uninstall` | `/remove` | update system packages or hackingtool · remove hackingtool and its tools | | `/clear` | `/cls` | clear the screen | | `/back` | `/b` | leave the current tool and go back | | `/help` | `/?`, `/h` | quick reference card | | `/quit` | `/q`, `/exit` | exit (also `q`, `Ctrl-C`, `Ctrl-D`) | | `@` | | open a tool (case-insensitive, fuzzy fallback) | | `@tag:` | | list and k from the tools carrying that tag |Inside a category: `1–N` k a tool · `97` install everything not yet installed · `98` archived tools · `99` back. Inside a tool: `1` install · `2` run · `c` ask for the exact command for your goal · `98` project page · `99` back./help — the same card, in the app. On a non-interactive terminal (or without `prompt_toolkit`) hackingtool falls back to the classic numbered menu, where `/` or `s` searches, `t` filters by tag, `r` or `a` recommends, `?` helps and `q` quits. Force it with `hackingtool --classic`.> **New here?** [docs/HOW-TO-USE.md](docs/HOW-TO-USE.md) walks through each of these > start to finish with numbered steps.---## Features ### ? `/find` — a tool for a need you don't have yetSearches the 215 curated tools first, then the GitHub search API, and ranks the results explainably. **Suggest-only** — it never clones, installs or runs anything — and it makes **zero model calls**./find crack a wpa handshakeIn your toolbox (vetted) • aircrack-ng (WiFi security suite) • Kismet (wireless detector / WIDS) • Reaver (WPS PIN attack) • WiGLE (wardriving map & API) • hashcat example hashes (WPA mode 22000)Found on GitHub — NOT vetted by uswifiphisher/wifiphisher 14713★ GPL-3.0 The Rogue Access Point Framework 14713★ · trusted author (ships in our catalog) · active · matches: security, wifi git clone https://github.com/wifiphisher/wifiphisher … Press `a` to keep a result: it is saved to `~/.hackingtool/found.yaml` as a "Discovered tools" entry — title, tags, description, link, and **no install or run command**, so a discovered entry can never execute anything. It shows up in your menu and in `/search` next launch.Out-of-scope asks (jamming, DoS, mass-targeting, malware) are refused **before any network call**, with an authorized alternative where one exists. Defensive/DFIR phrasing is never refused.Works anonymously at 10 GitHub searches/minute; a **no-scope, no-permission** token raises that to 30 — see [`/config github`](docs/HOW-TO-USE.md#7-add-a-github-token-for-find-config-github).### ? `/goal` — plan an objective, run it one step at a time /goal find live subdomains of example.com hackingtool drafts a short plan of real commands (with the reason for each step and an install hint for tools you don't have), asks you to confirm you are **authorized** to test the target, then walks the steps: `[y]` run · `[s]` skip · `[e]` edit · `[q]` abort. Every step runs list-form — never through a shell — and each goal gets a timestamped workspace under `~/.hackingtool/goals/` holding `plan.json`, a UTC-stamped `run.log`, and the raw output of each step.The model is called **once**, for planning; tool output is never fed back to it. With no model configured, `/goal` degrades to tool recommendations for the same objective.### ? Recommendations — say what you want in plain EnglishBare text (or `/ai`) maps intent to tools. The model may only return tags from the fixed taxonomy, and the catalog resolves tags → tools, so a tool can never be invented; with no model reachable a stdlib keyword matcher answers instead./ai — k one of the common tasks, or type the job in your own words. ### ? Tags and search`/tags` prints every tag in use with its live tool count; `@tag:` opens the tools carrying it; `/search ` matches names, descriptions and tags. /tags — 63 tags in use, with the number of tools behind each. ### ▶ Background panes (tmux)Long scans shouldn't block your console. With tmux installed, `/run … &` opens a labeled window in one detached `hackingtool` session: /run nmap -sV -oA scan 10.0.0.5 & ▶ started 'nmap' in background — /attach to view ` /panes` lists them, `/attach` watches one (`Ctrl-b` `d` to come back), `/kill ` or `/kill all` stops them, and the status line under the prompt shows `▶ N running`. No tmux? It says so and opens the tool inline instead; disable it entirely with `/config background_runner off`.### ⚙ Settings and the AI layer`/config` opens a full-screen settings editor (`↑↓` move, `←→` change, `Enter` edit, `t` test the connection, `Esc` close); `/config ` sets one key from the prompt. Settings live in `~/.hackingtool/config.json`.The AI layer is **opt-in and bring-your-own-key**: an OpenAI-compatible endpoint when `ai_base_url` + an API key are set, else a local [Ollama](https://ollama.com), else nothing — every feature degrades to a deterministic offline behaviour instead of guessing. Your API key is written only to `~/.hackingtool/.env` (mode 600), never to `config.json`, and never printed back. `/config test` reports the real failure if a probe fails.### ? Headless engagementsThe same catalog drives a non-interactive orchestrator that normalizes tool output into one `findings.json`: bash hackingtool --engagement acme --targets example.com --pipeline recon hackingtool --engagement acme --report # deterministic Markdown report hackingtool --engagement acme --ai-summary # opt-in triage of the REAL findings hackingtool --engagement acme --ai-report # opt-in narrative draft (report.draft.md) Out-of-scope targets are flagged and logged before anything runs, and the AI passes only ever summarize findings that exist.---## Documentation... {card-default label="? 工具信息" /} ? 项目地址:[https://github.com/Z4nzu/hackingtool](https://github.com/Z4nzu/hackingtool) ⭐ Star数:79344 ? 开发语言:Python ? 项目描述:面向黑客的一体化黑客工具 {/card-default}{cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool/archive/refs/heads/master.zip"} {cloud type="default" title="网盘下载" url="https://github.com/Z4nzu/hackingtool"}总的来说,**hackingtool**是一个功能比较实用的开源工具,适合日常工作和学习使用。如果你正在寻找一款相关工具,不妨下载试试。使用前建议仔细阅读项目文档。


Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
 /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858
Warning: Undefined array key "string_value" in /www/wwwroot/65gw.com/var/Widget/Base/Contents.php on line 858